We released ClickNix™, a free preemptive-security browser extension that protects everyday internet users from ClickFix attacks. ClickNix denies a ClickFix attack the chance to present itself, so the attack stops before the moment of deception.
What ClickFix does
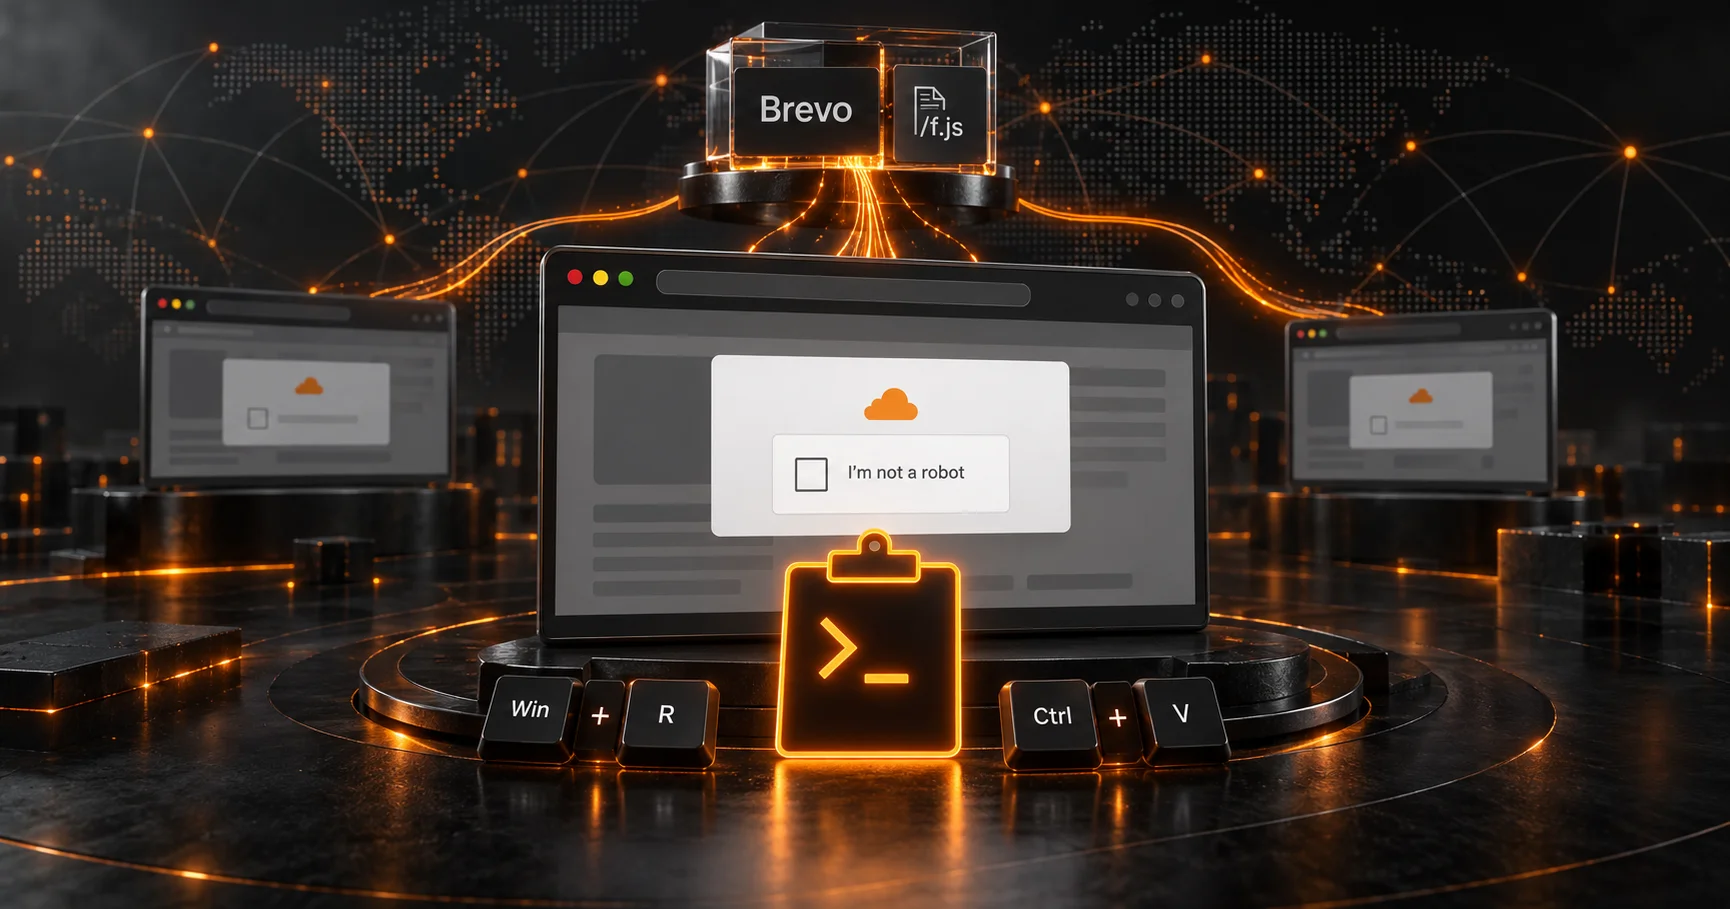
A ClickFix page lures the victim with what looks like a routine step: a CAPTCHA verification, a browser error message, a “fix this problem” prompt, or a fake meeting-software glitch. It then tells them to open the Windows Run dialog, a terminal or the Explorer address bar, paste a command, and press Enter. The technique combines social engineering (user deception) with “Living off the Land” (LotL) techniques. Because the victim runs the malicious command themselves, ClickFix sidesteps many of the email filters, antivirus signatures and endpoint controls that organizations rely on to catch conventional malware, and it defeats the detection-and-response model most current security tools depend on.
Recent campaigns put ClickFix on trusted platforms. Our joint research with HudsonRock exposed the PasteSwitch campaign, which used HBO Max’s official advertising account to deliver malware. Within 24 hours we tracked another major campaign in which Brevo’s own infrastructure delivered malware to victims through ClickFix.
The technique is growing:
- Check Point’s 2026 Cyber Security Report confirmed roughly a fivefold increase in ClickFix activity. The attack now spans Windows, macOS and Linux, and ready-made “ClickFix builder” kits circulate among threat actors of every skill level.
- We have seen every kind of adversary adopt it, from opportunistic infostealer and ransomware operators to nation-state-aligned groups. New variants keep appearing, including ones that fake a genuine browser crash to make the follow-on “fix” more convincing.
- In September 2026, our research of currently infected sites exceeded 25,000 unique domains.
- AI orchestration lets attackers set up campaign infrastructure quickly and build elaborate evasion, so ClickFix lures on trusted websites and platforms stay hidden from current security systems.
ClickFix does not rely on a technical exploit. It hijacks steps people have learned to treat as safe: proving they are human, fixing an error, following an IT-style instruction. Nothing malicious happens at the technical level until the user acts, which is why tools built to catch malicious files or known-bad URLs rarely see it.
“Exploiting the human means attackers are focusing their efforts on the weakest link in the security chain. But this relentless preying on vulnerable people is something we feel called to stop. ClickNix is an easy way we can help the world disrupt these attacks - especially for people who don’t have access to ZeroTrust connectivity yet,” said Francois Driessen, COO & CMO of ADAMnetworks.
How ClickNix responds
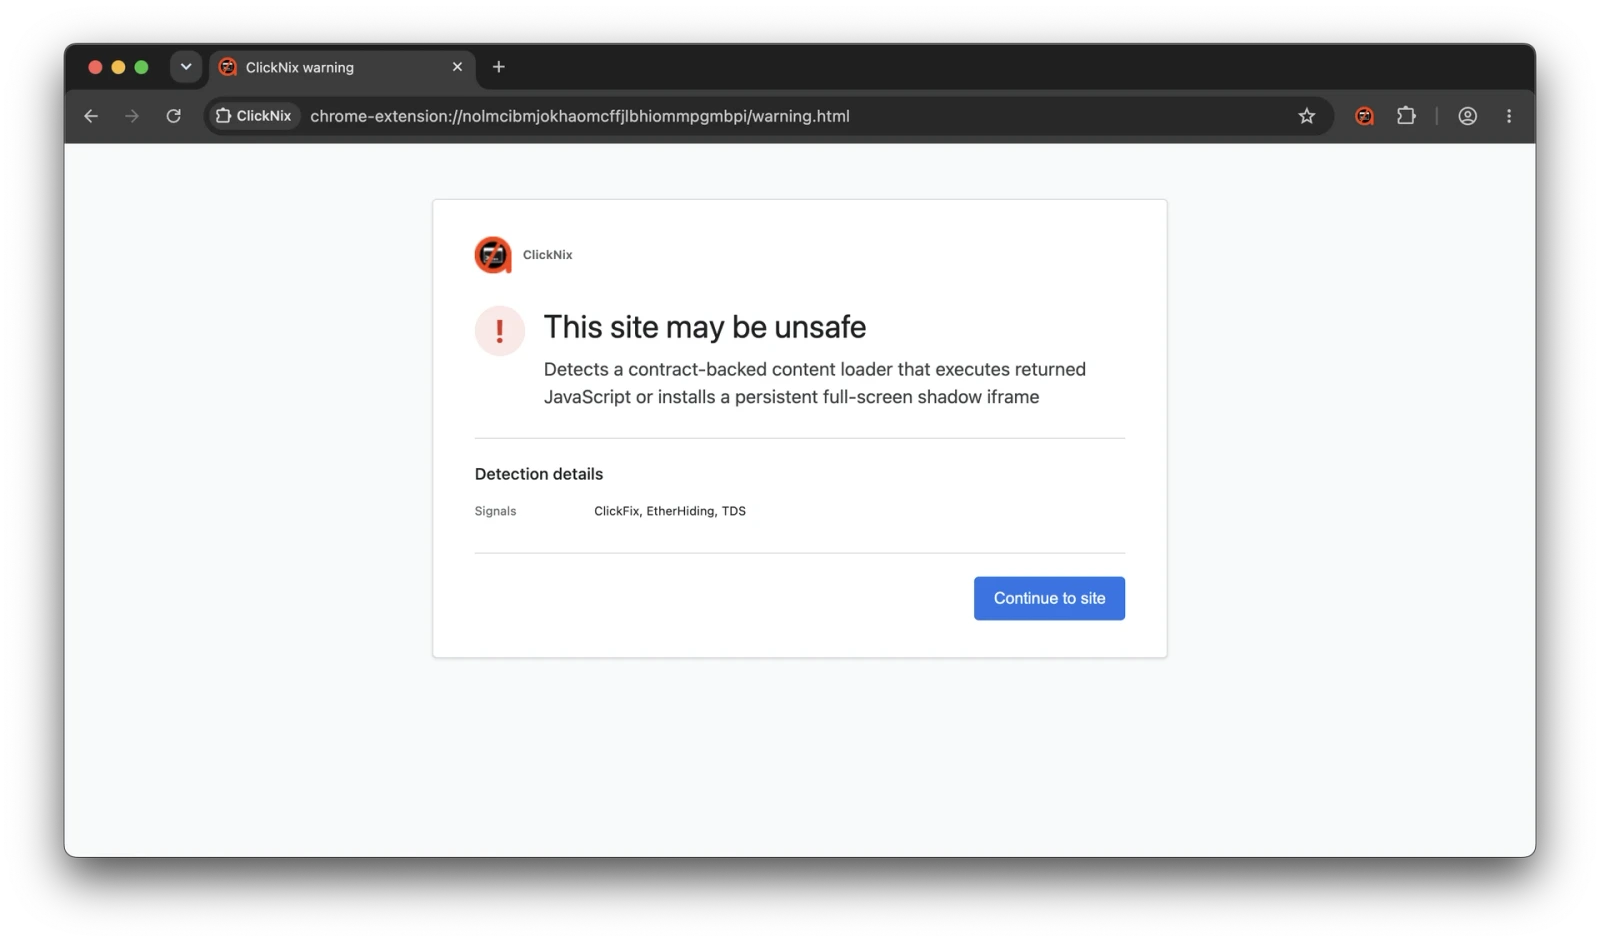
ClickNix applies our Preemptive Defense approach: disrupt the attack by design instead of detecting it after the page has loaded and started working on the user. As a page opens, ClickNix checks for known and predicted new ClickFix techniques. When it finds one, it blocks the content before it is displayed and warns the visitor that the site may be unsafe. If the lure never renders, there is no fake CAPTCHA to trust, no “fix” instruction to copy, and no command to run.
Each blocked attempt is reported to a central threat-intelligence database. Security teams, MSPs and our Preemptive Defense customers can subscribe to it, so an attack pattern intercepted for one ClickNix user becomes protection for everyone downstream, often before the same campaign reaches them.
“ClickFix attacks are winning right now because it attacks trust, not code — and most of the security industry is still relying on detection of harmful code,” said David Redekop, CEO & Founder of ADAMnetworks. “Preemptive Defense is our answer to that: we don’t wait for the moment of the attack to happen and then try to catch it. We take the moment away. ClickNix takes the core of that philosophy and puts it directly into a browser extension that anyone can install for free, because this isn’t a threat that should only be handled by people who can afford enterprise security. It’s hitting regular people, at scale, every day.”
We and our community partners also recheck every reported site to confirm whether the compromise has been fixed, and tell defenders when it is safe to allow the site again. A site owner whose site was hit by a ClickFix injection is not cut off for long after they clean it up.
Availability
Our network-level Preemptive Defense platform already disrupts a broad range of attacks for customers running Zero Trust Connectivity. ClickNix brings the same principle to individuals, families and small teams, with a narrow focus on ClickFix. It installs in seconds, needs no configuration, and runs in the background.
ClickNix is free for Chrome, Microsoft Edge and other Chromium-based browsers. A customizable enterprise-license version is available for defense technology providers and enterprise deployments that need a custom implementation. Install it from the ClickNix page.